 All Case Studies
Our threat monitoring clients see fewer alerts and catch the real ones metrics
Two recent managed detection and response engagements. Detection coverage and MTTR figures under MNDA; SOC walkthrough on a scoping call.
Cybersecurity and Compliance engagement,
Managed detection and response lead
Dcrayon tuned our SIEM detections to the MITRE ATT&CK map and staffed the SOC around mean time to respond. Analysts stopped drowning in false positives and started closing real incidents.
Managed detection and response build: SIEM detection tuning, EDR rollout, 24/7 SOC triage runbooks, and ATT&CK coverage mapping reviewed each month with the security lead.
Read Cybersecurity and Compliance engagement's Case StudyMid-market cybersecurity and compliance brand,
SOC and vulnerability management
Alerts piled up unread and we could not tell noise from a real breach. Dcrayon rebuilt our triage tiers and threat intelligence feeds, so the SOC now escalates what actually matters.
Threat monitoring paired with vulnerability management and log retention cleanup. A baseline detection audit mapped every critical asset to a SOC alert rule.
Read Mid-market cybersecurity and compliance brand's Case StudyWhy teams pick Dcrayon for SOC and MDR
Dcrayon has run 200+ solutions engagements for 60+ active retainers since 2016, from our Delhi HQ and Sheridan, Wyoming office. Our architects hold AWS, Azure, and GCP certifications, with CEH, OSCP, and CISSP analysts on staff. AI-first since the 2024 pivot.
Named lead analyst on every account
No unnamed queue of rotating staff. The analyst who tunes your detections owns the account and knows your alert history.
A detection Score before you commit
A written diagnostic and fixed estimate up front. You see your coverage gaps and scope before you sign, not after.
AI-assisted detection and triage
Every SOC engagement uses AI-assisted work: alert clustering, anomaly scoring against baselines, and analyst copilots for faster triage.
A monthly readout leadership can read
Weekly cadence plus a monthly report tied to one metric, like mean time to respond. Written for your CFO and your CISO alike.
HOW WE WORK
How Dcrayon works with the brands we partner with
A short film on how we work: the people you deal with, how we report, and the results we hold ourselves to.
What the SOC runs
Three layers of monitoring, measured by how fast something gets caught rather than how much it logs.
Step 1: Detection engineering
SIEM rules that fire correctly Log coverage mapped, then detections written and tuned against your environment so real events surface and noise does not.
Step 2: Endpoint and extended detection
EDR and XDR coverage Endpoint telemetry joined with network and identity signals, so an alert carries the context needed to judge it.
Step 3: Analyst-led triage
Round the clock Human analysts investigate and escalate with threat intelligence enrichment, working with or without your in-house team.
Detection signals our SOC engineers and tunes
Standard on every Dcrayon SOC and MDR engagement
Each detection below maps to a MITRE ATT&CK technique and a measurable factor in your stack, tuned and verified by the lead analyst on your account.
SOC 2-ready audit trail
Every detection rule and response ships with an audit trail: change log, tuning rationale, updated runbook, and evidence SOC 2 audit firms can review.
AI-assisted alert triage
DcrayonAI clusters related alerts, scores anomalies against your baseline, and flags detection drift so analysts spend time on real threats.
Log volume and cost control
We tune log ingestion so you pay for signal, not noise.
Monthly readouts report cost per monitored endpoint and per detection, not just SIEM spend.
Compliance mapping overlay
Every detection maps to a control in SOC 2, ISO 27001, and GDPR, so your monitoring evidence lines up with the next audit.
Three methods we run on every SOC and MDR engagement
Score, Sequence, Repair. A detection-coverage diagnostic, a 90-day rollout plan, and an AI-assisted toolkit we run on every SOC engagement.
Growth Intelligence (detection coverage axis)
A 150-signal review of your detection stack. We map log source coverage, SIEM rule quality, EDR reach, alert triage speed, and mean time to respond against MITRE ATT&CK technique gaps. Free on every proposal call.
Dcrayon Sequence (detection rollout plan)
A 90-day playbook that sequences onboarding, log source integration, and rule tuning back to one metric you pick, such as mean time to detect.
DcrayonAI (detection toolkit)
An internal toolkit that audits your current detections against MITRE ATT&CK and drafts a prioritized coverage roadmap your CFO can budget.
How our SOC runs day to day
Three repeatable plays that tighten detection coverage across cycles.
Step 1: Score
A free Growth Intelligence readout in one business day. We rate your log coverage, detection rules, and response runbooks, then hand you a single 0-100 number and the exact blind spots an attacker would use first. No follow-on commitment.
Step 2: Plan
A written 90-day monitoring plan built around one metric you name, like mean time to detect or alert noise reduction. A senior SOC architect writes the detection logic, every SoW carries a mutual exit clause, and nothing locks you into an annual term.
Step 3: Compound
A weekly working session with your SOC architect plus a monthly summary your CFO can follow. The work stacks: tuning detections in cycle one cuts alert noise in cycle two, which frees analysts for real threat hunting in cycle three.
Get a detection coverage readout
A written review of your log coverage, detection rules and response paths, with a fixed estimate, in one business day.
Other Cybersecurity and Compliance solutions
Sibling Dcrayon services inside the Cybersecurity and Compliance category. Programs clients often layer alongside Threat Monitoring.
WHY DCRAYON
Why teams put monitoring with us
Four commitments that decide whether monitoring is useful or just loud.
Dwell time is the measure
We report mean time to detect and respond. Raw alert counts describe how noisy a tool is, not how safe you are.
A named lead analyst
No unnamed queue of rotating staff. The analyst who tunes your detections owns the account and knows your estate.
Tuning is continuous
Detections get reviewed as your environment changes, because rules written once quietly stop matching reality.
A monthly readout leadership can read
One metric, such as mean time to respond, reported monthly in language that does not need a security background.
Real client work, with the receipts
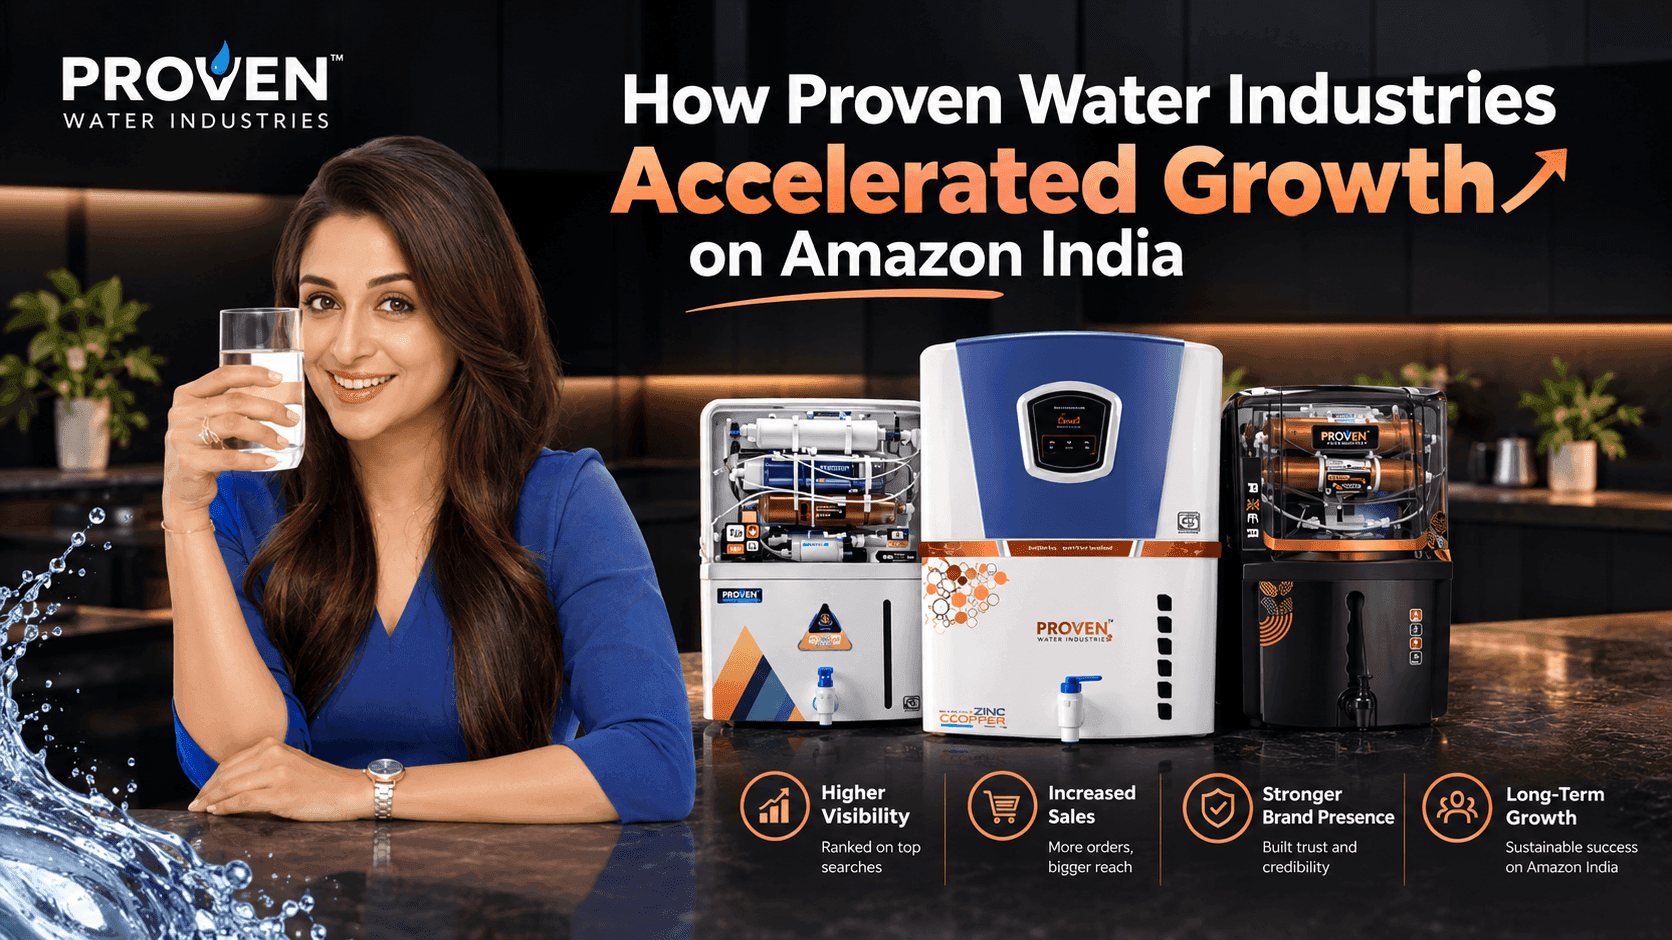
200%
Improvement in conversion performance
Proven Water Industries
Proven's growth on Amazon over the engagementDcrayon's work on Proven's Amazon account has run as a long-term growth programme rather...
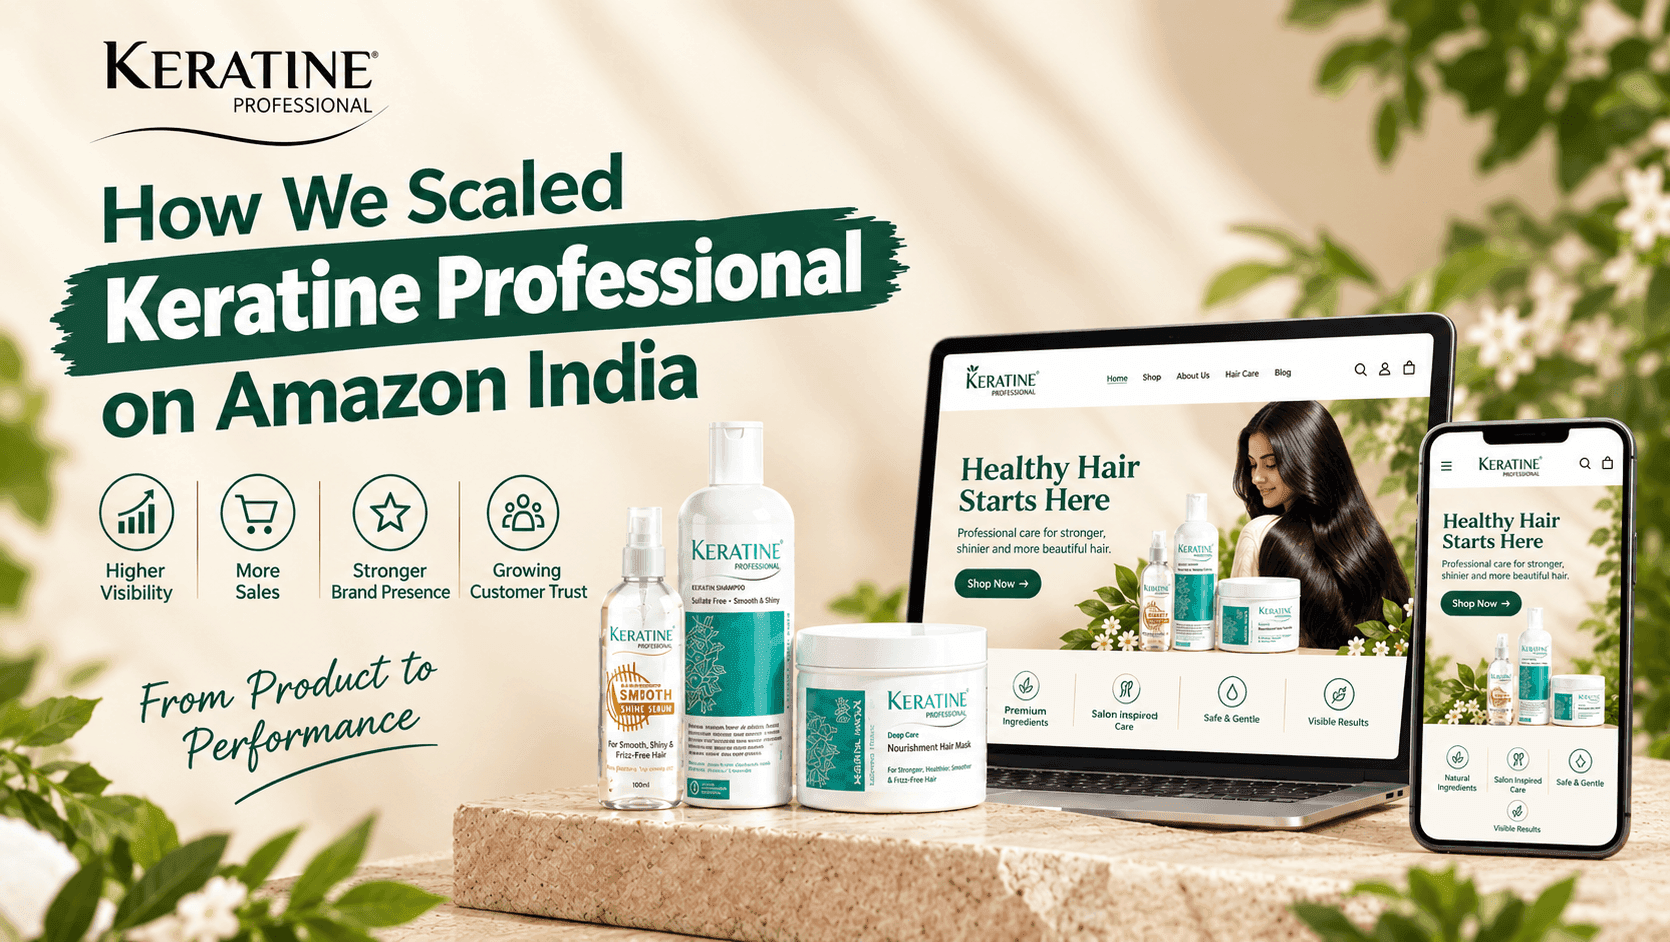
Keratine Professional
What is in place on Keratine Professional's accountOn Amazon.in today, the brand's lead listings name the product type, the hair concern...
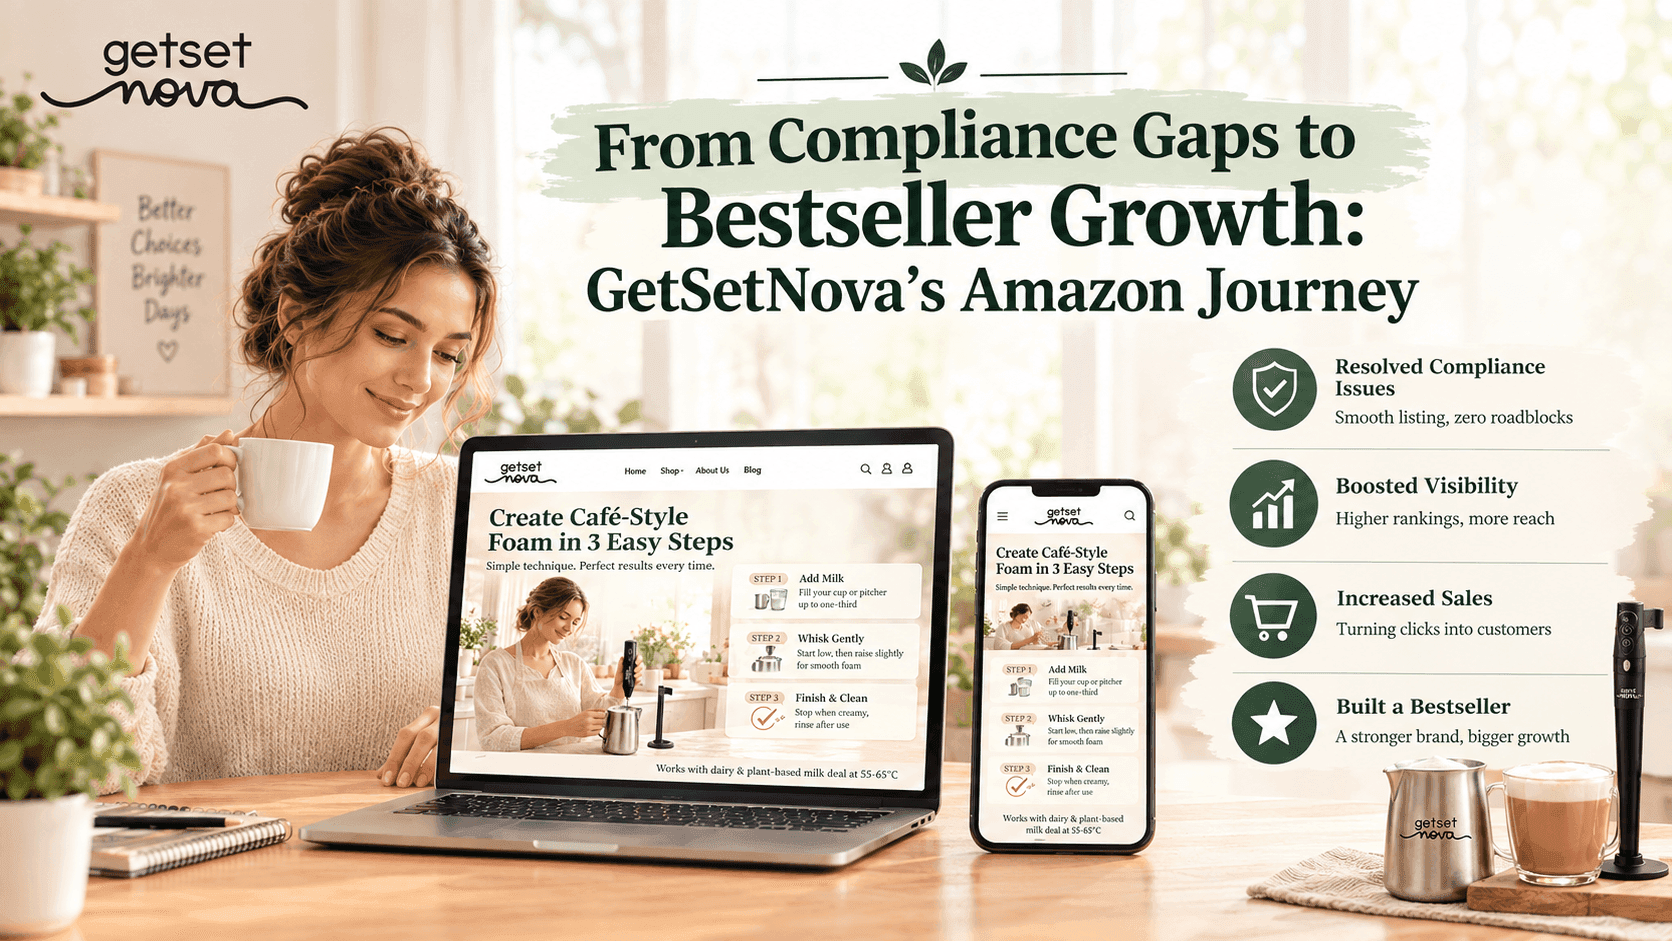
3,400%
Sales growth on Amazon India
GetSetNova
Sales up 3,400% on Amazon IndiaOver the engagement, GetSetNova's sales on Amazon India are up 3,400%, and the brand holds Amazon Best...
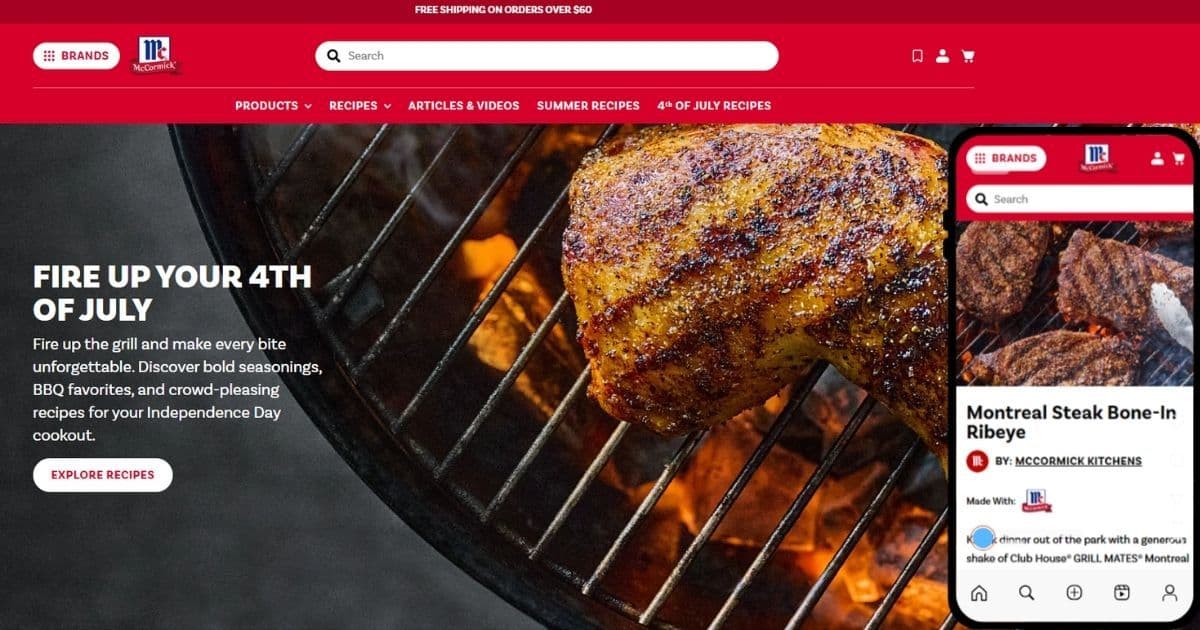
McCormick & Company
What changed on McCormick's front endThe front end now loads non-essential scripts after the main content, runs third-party tags through...
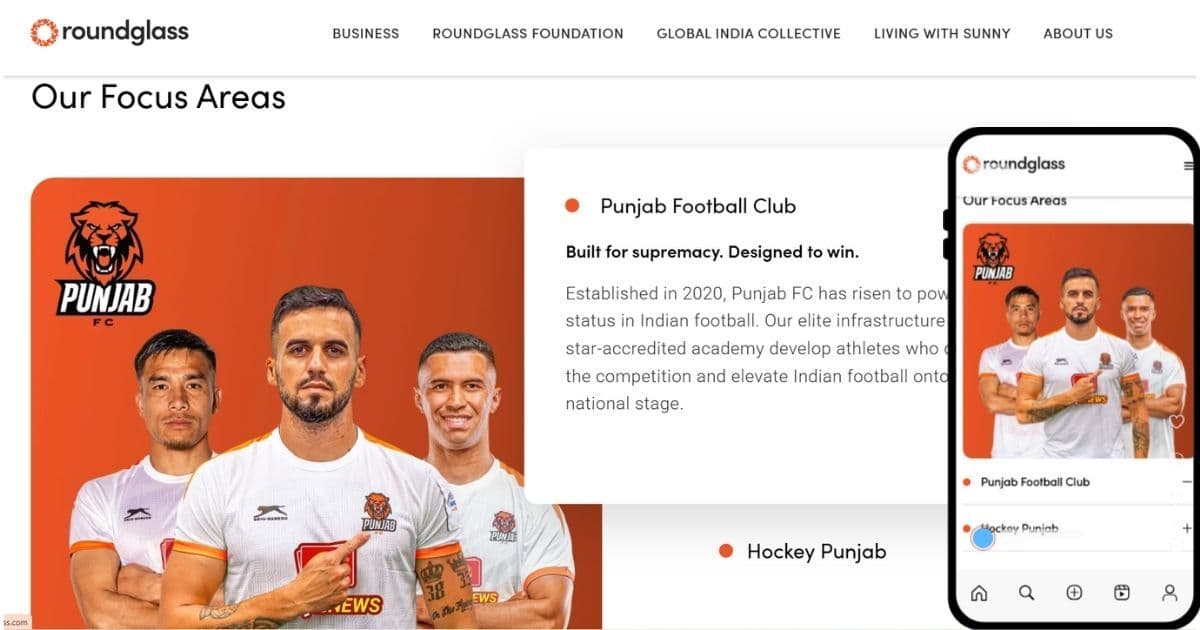
Roundglass
What changed for Roundglass's HR team, IT and new employeesAccount creation, group membership and licence assignment now follow the...
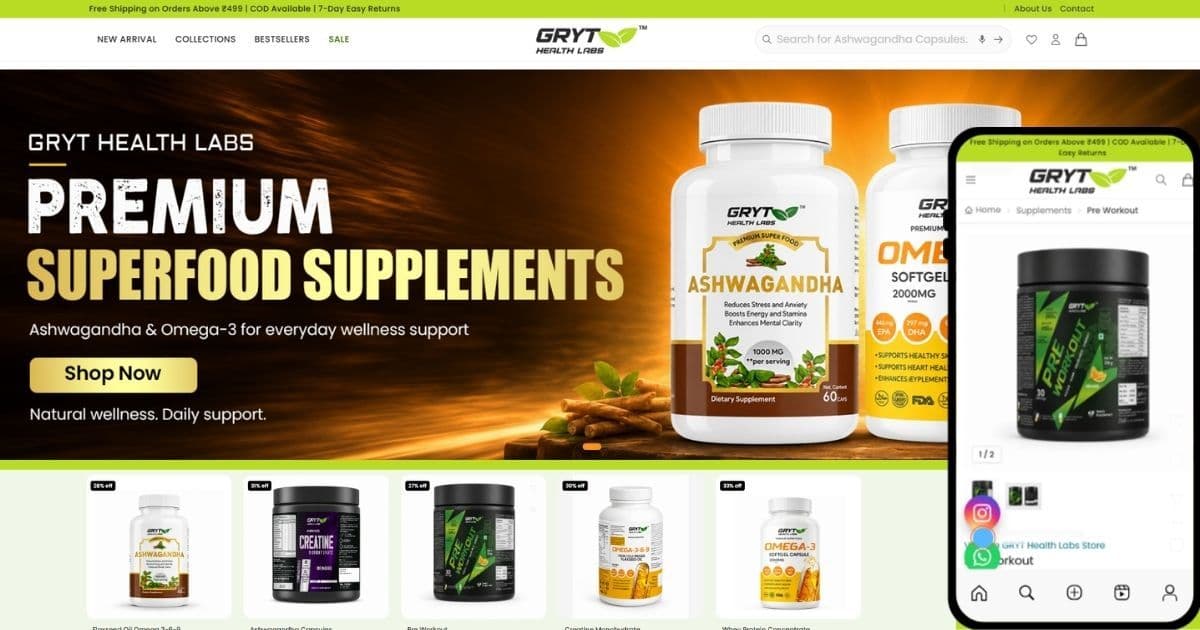
GRYT Health Labs
What GRYT shoppers can do on the storeShoppers can check the brand's licence and ownership details, compare single units with packs of...
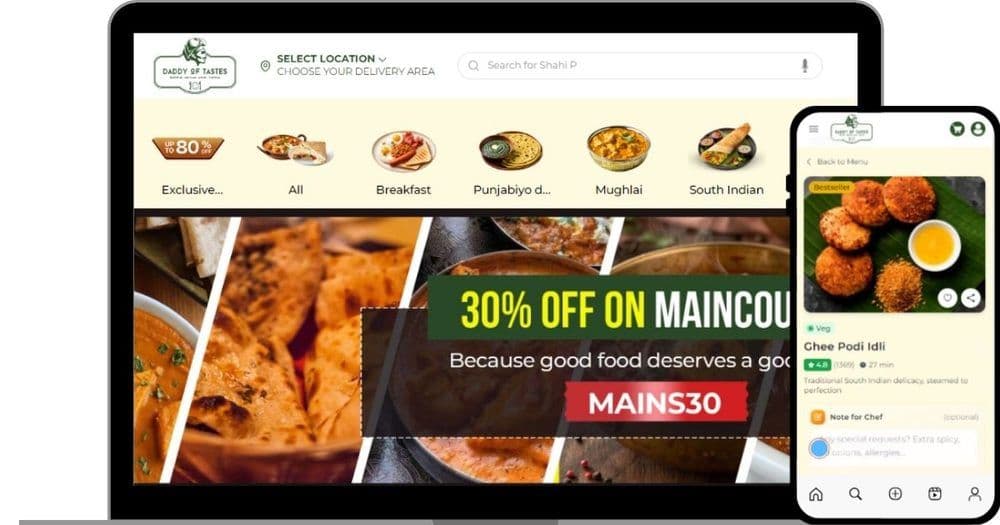
Daddy of Tastes
What the Daddy of Tastes kitchens and riders work withCustomers can order from the full menu, pin their exact location, pay through...
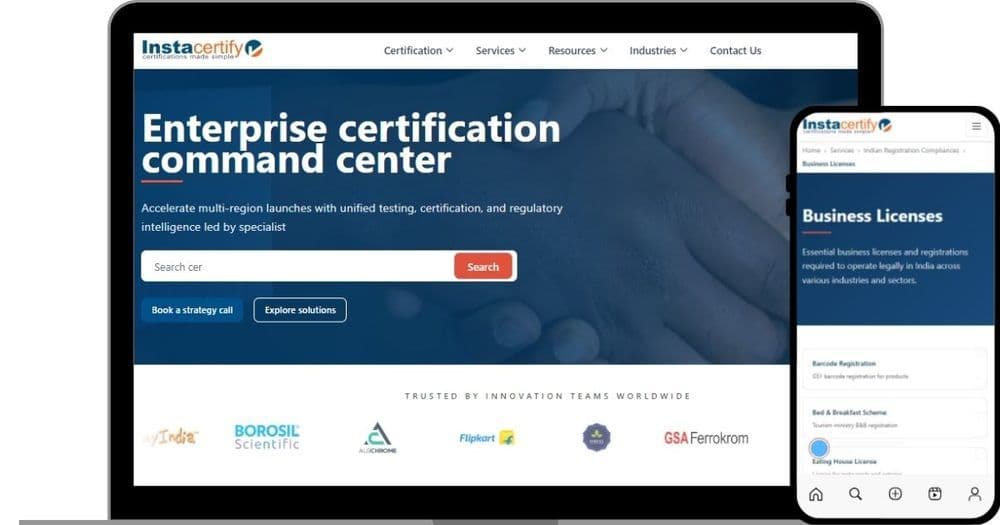
Instacertify
What Instacertify's visitors could doVisitors could search for a certification from the first screen, see two clear next steps, and move...
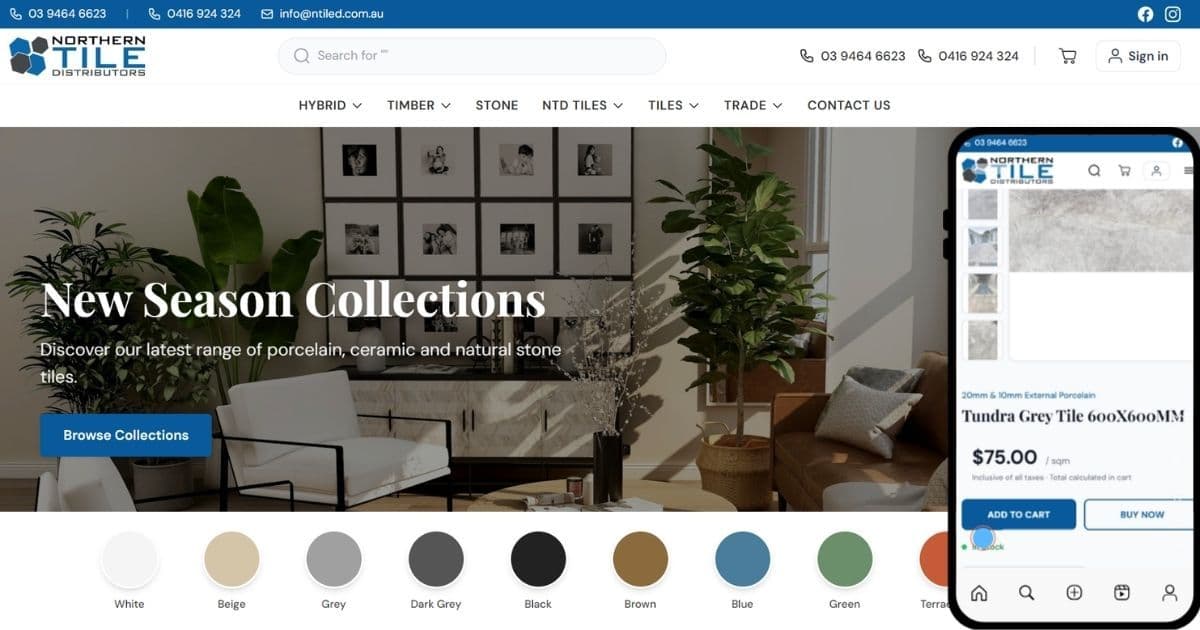
Northern Tile Distributors
The storefront delivers a clean shopping experience on both desktop and mobile. Page load times improved significantly, the add-to-cart rate...
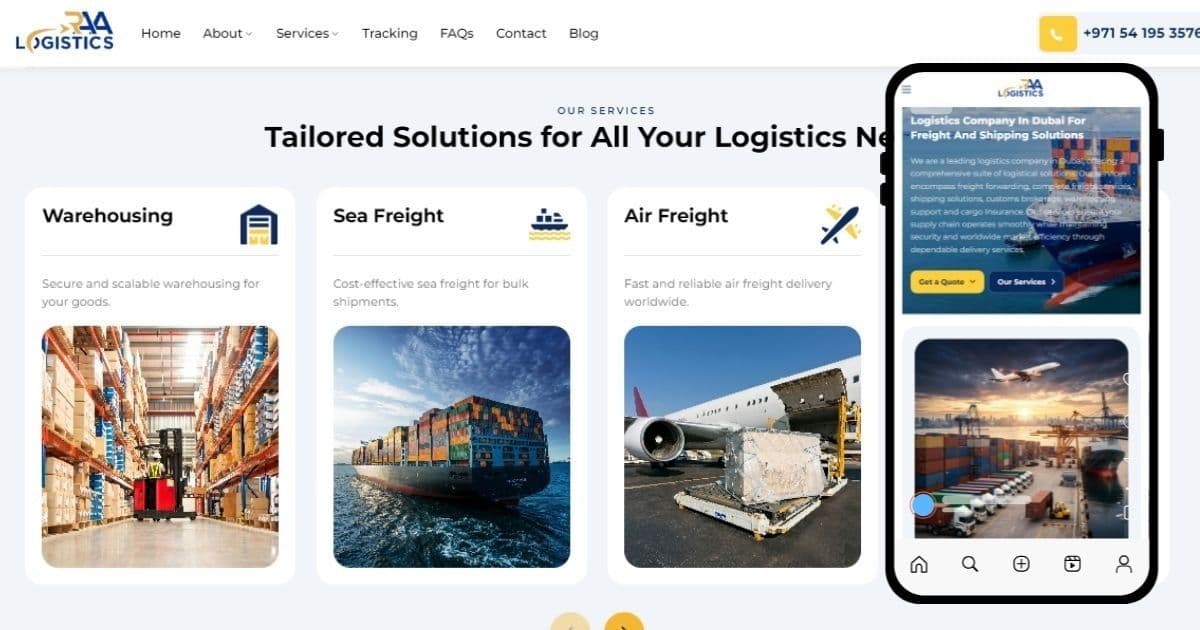
RAA Logistics
What RAA's customers and team have nowProspective customers can find the exact service they need, read what it covers, see who runs the...
The detection Score is free. The 90-day SOC plan is yours to keep.
Across our 60+ active solutions retainers, the median 12-month cost of running without managed detection and response for teams we measure sits in the Rs 6L to Rs 90L band. Book the scoping call to size yours.
Free Dcrayon detection-coverage Score, mapped to your log sources
Written 90-day SOC plan tied to one metric, such as mean time to detect
A mutual exit clause in every SoW, no annual lock-in
A named lead analyst on your account from the first shift
SOC and Threat Monitoring FAQs
Onboarding runs in stages: log source access first, then baseline tuning, then live monitoring. Urgent post-incident work is prioritized ahead of the standard queue.
Both. Some clients hand us the whole SOC as their managed detection and response team; others keep an internal analyst team and use us as senior architect plus after-hours escalation. We scope per account.
Most SOC and MDR engagements start at Rs 4 to 8 lakhs per month in India, or USD 6 to 15 thousand per month globally. Audit-only and SOC 2 readiness work starts lower.
Yes. We run a free detection-coverage Score on your proposal call, with your top gaps ranked. No follow-on commitment required.
Ready to Grow Your Business?
Get expert digital marketing that delivers measurable results. Free consultation available.
We will review how your search, paid and marketplace channels are performing, and point out the gaps costing you the most right now.
You will finish the call knowing what to fix first, whether or not you work with us.