 All Case Studies
Our GDPR audit clients close findings before the regulator asks metrics
Two recent GDPR audit engagements. Article 30 records and DPIA gaps documented under MNDA; a walkthrough is available on a scoping call.
Cybersecurity and Compliance engagement,
Lead data protection consultant
Dcrayon mapped every processing activity against Article 30 and ranked our gaps by real breach exposure, not a generic checklist. We closed the priority findings and reported them to counsel.
GDPR audit: a data protection consultant reviewed lawful basis, records of processing, DSAR workflow, and standard contractual clauses for third-country transfers, with a prioritized remediation log for the DPO.
Read Cybersecurity and Compliance engagement's Case StudyMid-market cybersecurity and compliance brand,
GDPR compliance consultant, cookie and consent review
Our cookie consent and DSAR handling had drifted out of compliance for more than a year. Dcrayon re-scoped the audit around our riskiest processing and gave us a remediation plan we could act on.
GDPR audit paired with a cookie and consent review across the site. An opening gap assessment set the baseline against ICO guidance and post-Schrems II transfer rules.
Read Mid-market cybersecurity and compliance brand's Case StudyWhy choose Dcrayon for GDPR Compliance Audit
Dcrayon has run privacy and security engagements for 60+ active retainers since 2016, from our Delhi HQ and Sheridan, Wyoming office. Our data privacy consultants work daily with Article 30 registers, DPIAs, and Schrems II transfer rules, backed by CEH, OSCP, and CISSP security staff.
A named data protection consultant on every account
No trainees learning privacy law on your budget. The GDPR compliance consultant who scopes the audit stays with you through remediation.
A structured GDPR gap score up front
A written gap diagnostic and a fixed estimate before you commit. You see the scope and the risks ranked before signing anything.
Automated data discovery, not manual spreadsheets
Every audit uses automated scanning to find personal data across your stack, so nothing hides in a forgotten database or spreadsheet.
Reporting your legal team can act on
Weekly sessions plus a monthly readout that maps every open gap to a specific GDPR or DPDP obligation, in language your legal and product teams can act on.
HOW WE WORK
How Dcrayon works with the brands we partner with
A short film on how we work: the people you deal with, how we report, and the results we hold ourselves to.
What the audit produces
Three deliverables that turn a compliance question into a plan with owners and dates.
Step 1: Gap analysis and data mapping
EU, UK and DPDP 2023 Automated discovery finds personal data across your stack, then each finding is mapped to the clause it breaches.
Step 2: Records of processing and impact assessments
Documents that match reality ROPA and DPIA documentation written from how your systems actually work, not filled in from a template.
Step 3: A prioritised remediation roadmap
Ranked by risk Every gap gets an owner, an effort estimate and a rank, so the highest-risk items close first rather than the easiest.
The controls our GDPR compliance audit puts under review
What every Dcrayon GDPR compliance audit includes by default
Each check below maps to a specific GDPR or DPDP obligation, reviewed by the data protection consultant assigned to your account.
Documented evidence trail
Every finding ships with the evidence a regulator expects: an updated ROPA, DPIA records, consent logs, and a dated register of remediation actions.
Continuous data discovery
Automated scanners map personal data across your databases, SaaS tools, and file stores, flagging new collection points before they become blind spots.
Data minimization by design
We flag personal data you no longer have a lawful basis to hold, then set retention schedules so it is deleted on time rather than kept by default.
Cross-border transfer checks
Every data flow leaving the EU or UK is checked for a valid transfer mechanism: Standard Contractual Clauses, the UK IDTA, or adequacy, with a transfer impact assessment on file.
Three frameworks we run on every GDPR Compliance Audit engagement
A compliance gap score, a prioritized remediation roadmap, and automated data discovery, run on every GDPR compliance audit.
Growth Intelligence (GDPR gap index)
Five-axis 150-point review. The GDPR axis maps your Article 30 records of processing, the lawful basis behind each activity, DSAR handling, cross-border transfer safeguards, and breach-response readiness. Free on every proposal call.
Dcrayon Remediation Roadmap (audit sequencing)
A roadmap that ranks each gap by regulatory risk and effort, so the highest-exposure items, like DSAR handling or consent, get fixed first.
DcrayonAI (data discovery toolkit)
Our tooling scans your systems for personal data, maps it to processing purposes, and drafts the ROPA and DPIA records regulators ask to see.
How Dcrayon runs GDPR compliance services
Three habits that keep your GDPR and DPDP compliance current as your data and vendors change.
Step 1: Score
A free Growth Intelligence readout of your GDPR posture. A five-axis review scored against your real processing activities gives one number from 0 to 100, plus the gap list of obligations still open. No follow-on commitment.
Step 2: Plan
A written 90-day GDPR remediation plan tied to one compliance goal you pick, such as closing DSAR gaps or fixing consent capture. A senior data protection consultant owns the register, and every SoW stays month to month with no annual lock-in.
Step 3: Compound
A weekly working session with your data protection consultant, plus a monthly summary your legal and finance leads can both read. Early cycles close the ROPA and lawful-basis gaps; later cycles firm up consent, retention schedules, and processor contracts.
Get a GDPR gap report
A written gap diagnostic scored against your real processing activities, with a fixed estimate before you commit.
Other Cybersecurity and Compliance solutions
Sibling Dcrayon services inside the Cybersecurity and Compliance category. Programs clients often layer alongside GDPR Compliance Audit.
WHY DCRAYON
Why teams run the audit with us
Four commitments behind every GDPR engagement.
Every gap cites its clause
Findings map to a named GDPR or DPDP article, so your legal team can act on the report without re-deriving the argument.
Discovery is automated, not surveyed
We scan for personal data across the stack rather than asking teams to remember. Questionnaires miss the copies.
A named data protection consultant
No trainees learning privacy law on your budget. The consultant who scopes the audit is the one who delivers it.
Fixed scope and fixed price
A written scope and a fixed estimate before the audit starts, so the cost of finding out is known in advance.
Real client work, with the receipts
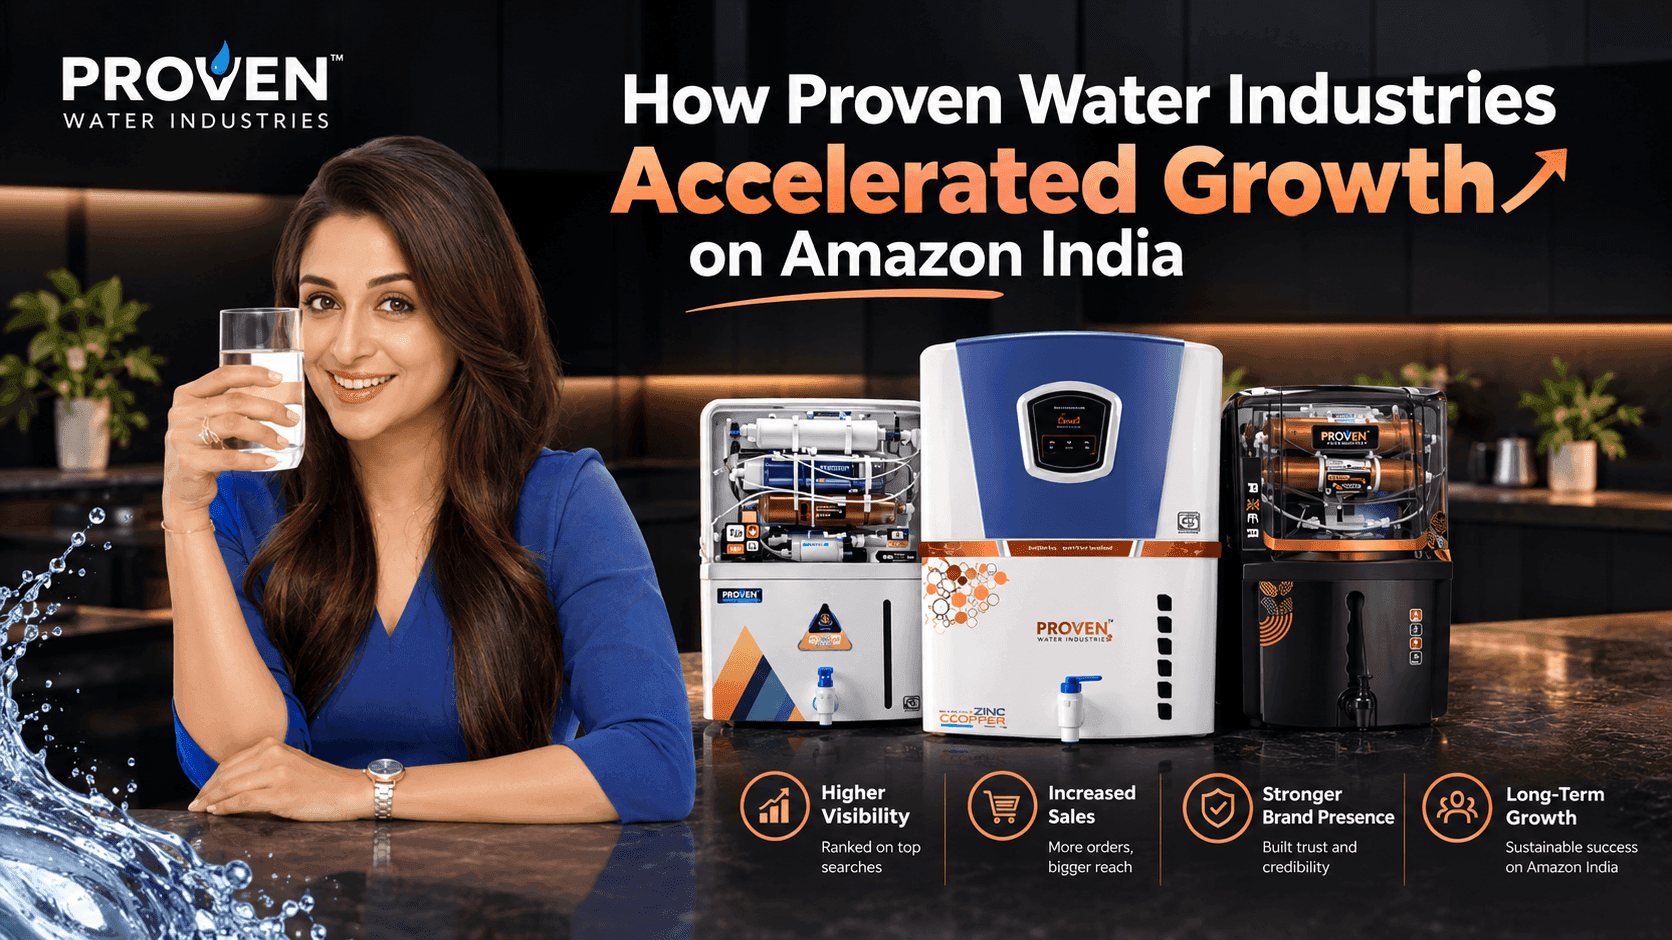
200%
Improvement in conversion performance
Proven Water Industries
Proven's growth on Amazon over the engagementDcrayon's work on Proven's Amazon account has run as a long-term growth programme rather...
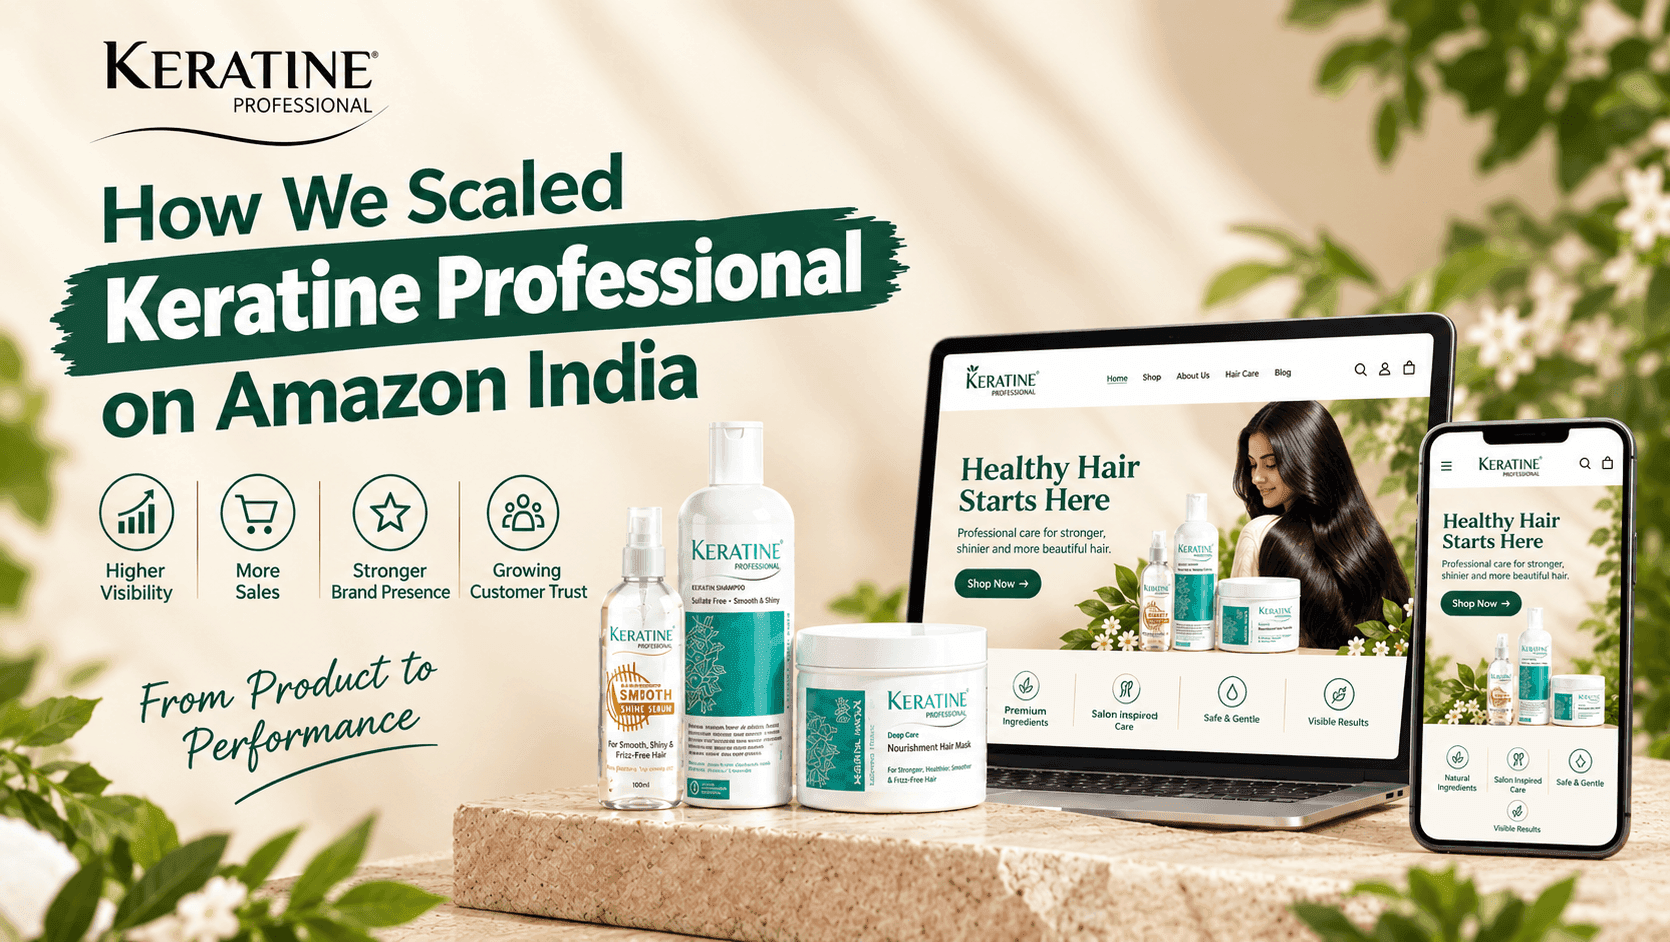
Keratine Professional
What is in place on Keratine Professional's accountOn Amazon.in today, the brand's lead listings name the product type, the hair concern...
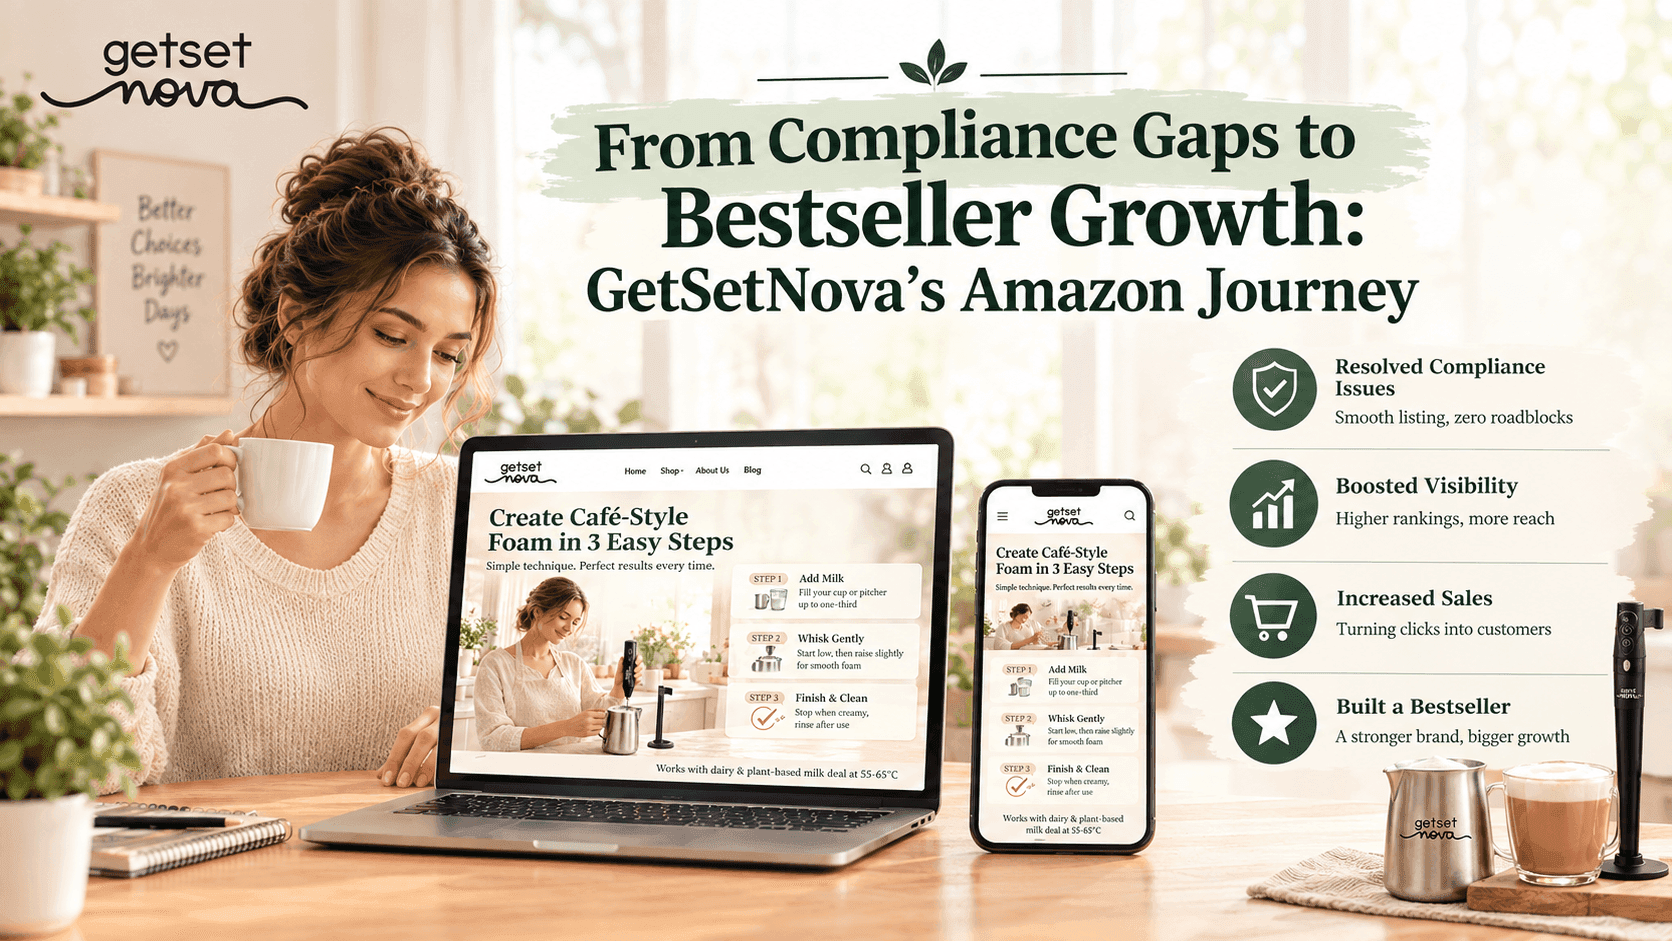
3,400%
Sales growth on Amazon India
GetSetNova
Sales up 3,400% on Amazon IndiaOver the engagement, GetSetNova's sales on Amazon India are up 3,400%, and the brand holds Amazon Best...
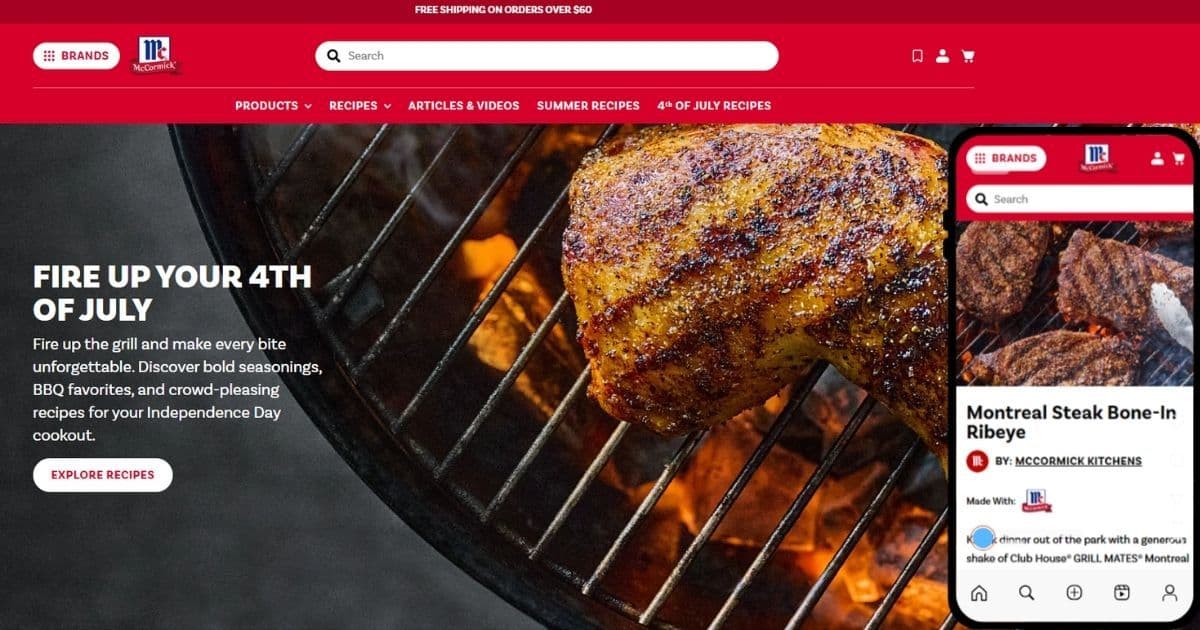
McCormick & Company
What changed on McCormick's front endThe front end now loads non-essential scripts after the main content, runs third-party tags through...
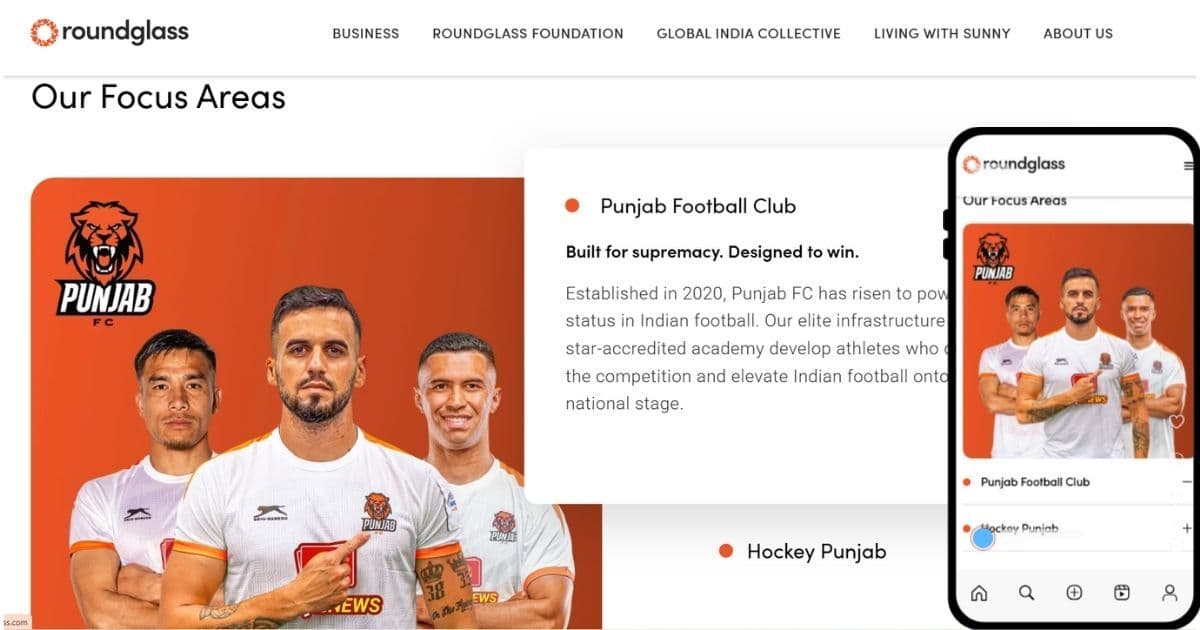
Roundglass
What changed for Roundglass's HR team, IT and new employeesAccount creation, group membership and licence assignment now follow the...
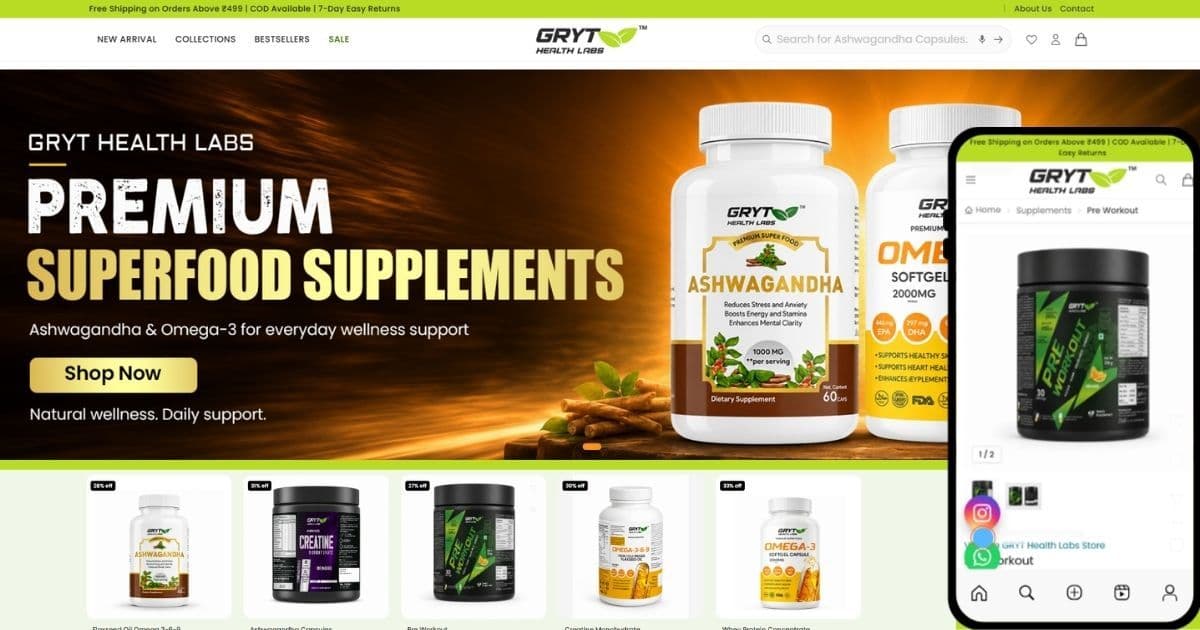
GRYT Health Labs
What GRYT shoppers can do on the storeShoppers can check the brand's licence and ownership details, compare single units with packs of...
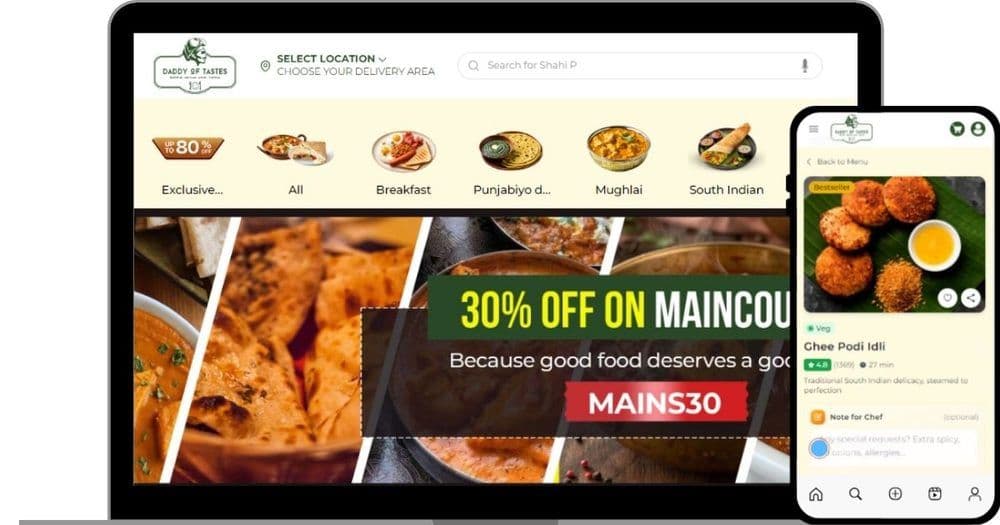
Daddy of Tastes
What the Daddy of Tastes kitchens and riders work withCustomers can order from the full menu, pin their exact location, pay through...
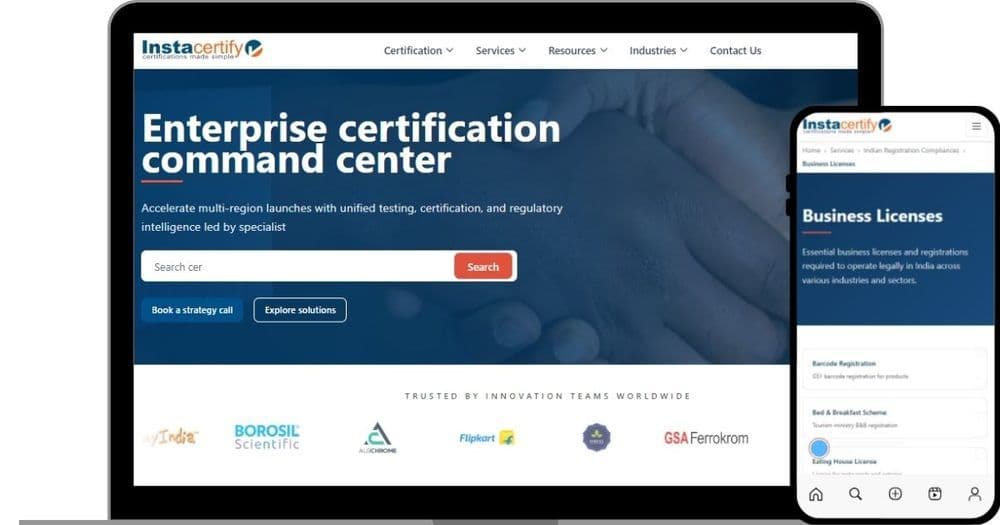
Instacertify
What Instacertify's visitors could doVisitors could search for a certification from the first screen, see two clear next steps, and move...
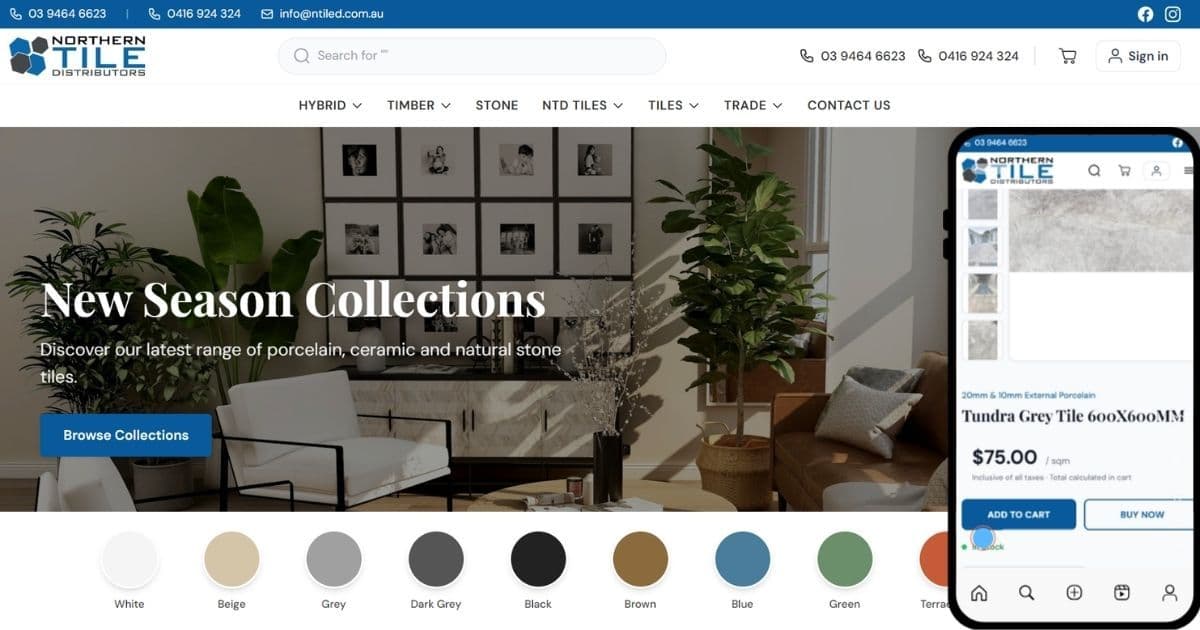
Northern Tile Distributors
The storefront delivers a clean shopping experience on both desktop and mobile. Page load times improved significantly, the add-to-cart rate...
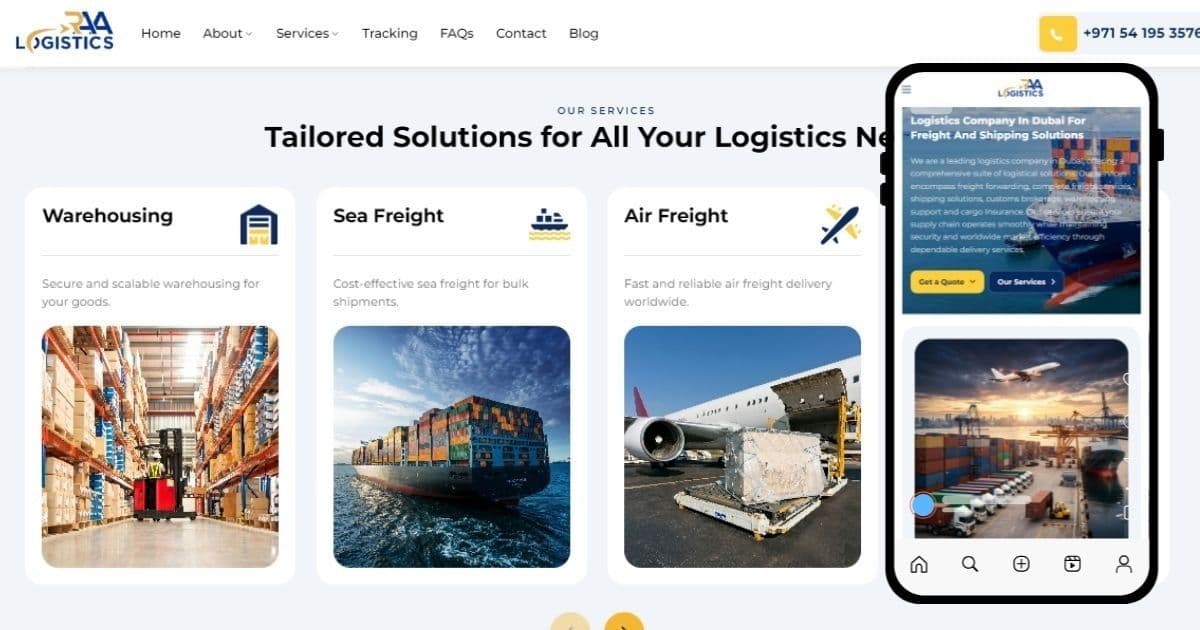
RAA Logistics
What RAA's customers and team have nowProspective customers can find the exact service they need, read what it covers, see who runs the...
The GDPR gap score is free. The remediation plan is yours to keep.
Across our 60+ active retainers, the median 12-month exposure we measure for teams running without a structured GDPR program, from missed DSAR deadlines to undocumented transfers, lands in the Rs 6L to Rs 90L band. Book the scoping call to size yours.
Free Dcrayon GDPR compliance gap score, mapped to your data flows
Written remediation roadmap, ranked by regulatory risk
Mutual exit clause in every SoW, no annual lock-in
A named data protection consultant on your account throughout
GDPR Compliance Audit FAQs
Onboarding opens with a data-mapping workshop and access to your systems and vendor contracts. Post-breach reviews take priority over routine gap audits in the queue.
Both. Some clients hire us as their outsourced data protection function; others use us as their senior GDPR compliance consultant plus escalation alongside an internal DPO. We scope per account.
Most GDPR compliance services start at Rs 4 to 8 lakhs per month in India, or USD 6 to 15 thousand per month for global clients. A one-off audit of your processing activities and consent setup starts lower.
Yes. A free GDPR gap score on your proposal call, mapped to your main data flows. No follow-on commitment required.
Ready to Grow Your Business?
Get expert digital marketing that delivers measurable results. Free consultation available.
We will review how your search, paid and marketplace channels are performing, and point out the gaps costing you the most right now.
You will finish the call knowing what to fix first, whether or not you work with us.