 All Case Studies
Our security audit clients close findings before the next control review metrics
Two recent information security audit engagements. Findings register and remediation status shared under MNDA on a scoping call.
Cybersecurity and Compliance engagement,
Information security audit lead
Dcrayon ran our security audit against ISO 27001 Annex A and CIS Benchmarks, not a generic checklist. Every finding came with an owner, a severity rating, and a fix we could verify.
Information security audit: control gap assessment against ISO 27001 and NIST CSF, config and access review, prioritized findings register with named remediation owners.
Read Cybersecurity and Compliance engagement's Case StudyMid-market cybersecurity and compliance brand,
Security audit and penetration testing lead
Our last audit was a PDF nobody actioned. Dcrayon gave us a live findings register, mapped each control to CIS and SOC 2, and re-tested every fix we closed.
Security audit paired with penetration testing and policy review. A baseline scan with Nessus plus manual config checks set the starting posture across the systems in scope.
Read Mid-market cybersecurity and compliance brand's Case StudyWhy teams pick Dcrayon as their security audit company
Dcrayon has shipped 200+ solutions engagements for 60+ active retainers since 2016, from our Delhi HQ and Sheridan, Wyoming office. Our auditors hold CEH, OSCP, and CISSP and work across AWS, Azure, and GCP.
A senior auditor on every account
No trainees testing your systems for practice. The senior auditor who scopes your security audit runs the testing and signs the report.
Manual testing, not just a scan
Scanners catch the easy issues. Our auditors chain findings by hand to show what a real attacker could reach and what that access would cost you.
CERT-In aligned method
We follow CERT-In and OWASP testing guidance, so your audit report holds up with regulators, insurers, and enterprise procurement teams.
Board-ready reporting
Two reports from one audit: a technical findings register for engineers, and a plain-English risk summary your board can act on.
HOW WE WORK
How Dcrayon works with the brands we partner with
A short film on how we work: the people you deal with, how we report, and the results we hold ourselves to.
What the audit covers
Vulnerability assessment and penetration testing across four layers, ranked by exploit risk rather than by count.
Step 1: Application and network
Authenticated VAPT Authenticated scanning plus manual testing across your applications and network, with findings CVSS-scored.
Step 2: Cloud configuration and identity
Where the real gaps are Cloud config, IAM roles and privilege paths reviewed, since most breaches now start with identity rather than a missing patch.
Step 3: A remediation plan with owners
Ranked, not listed Every finding gets a named owner and a rank, so the register becomes a plan instead of a backlog nobody opens.
What a Dcrayon security audit actually inspects
What comes standard in a Dcrayon security audit
Each item below is checked by hand and confirmed by the lead auditor on your account, never left to an automated scanner alone.
Traceable findings register
Every finding lands in a register with a CVSS score, the affected asset, a proof of concept, remediation steps, and a retest column.
Continuous config monitoring
Our tooling watches cloud config drift against CIS benchmarks and flags new public buckets, open ports, and over-privileged IAM roles.
Ranked by risk, not by noise
We rank issues by real exploitability and business impact, so you fix the handful an attacker would use first, not a raw scanner dump.
Compliance mapping
Findings map to ISO 27001 Annex A, SOC 2, and GDPR controls, so one audit feeds both your certification evidence and your security backlog.
The three deliverables behind every Dcrayon security audit
A baseline risk score, a prioritised fix plan, and a retest that confirms each closed issue actually stays closed.
Dcrayon Risk Score (security posture)
A 150-point security review across five areas. The audit checks your external attack surface, access controls, patch levels, encryption, and logging against OWASP and ISO 27001 baselines. Free on every proposal call.
Dcrayon Remediation Plan (fix sequencing)
A ranked fix plan that puts the highest-risk findings first and names an owner and a verification step for each one.
Dcrayon AI (audit toolkit)
In-house tooling that runs SAST, DAST, and dependency scans, then drafts a remediation roadmap your finance team can budget against.
How a Dcrayon security audit works
Three repeatable steps that keep your security posture improving audit after audit.
Step 1: Score
A free Growth Intelligence readout in one business day. We run an authenticated vulnerability scan, rank findings by CVSS severity, and give you one 0-100 number plus the full gap list. No follow-on commitment.
Step 2: Plan
A written 90-day remediation plan tied to one risk metric you pick, such as open critical findings. A senior security architect owns the testing, and every SoW lets either side stop. No annual lock-in.
Step 3: Compound
Weekly working sessions with your senior architect and a monthly readout your finance team can read. Each cycle builds on the last: patch and config fixes first, then a retest to confirm the critical findings are closed.
Get a security audit readout
An authenticated scan and a written diagnostic of your exposure, with a fixed estimate, in one business day.
Other Cybersecurity and Compliance solutions
Sibling Dcrayon services inside the Cybersecurity and Compliance category. Programs clients often layer alongside Security Audit.
WHY DCRAYON
Why teams pick us as their security audit company
Four commitments behind every audit we deliver.
Findings ranked by exploit risk
Severity reflects what an attacker could actually chain together, not the default rating a scanner printed.
Manual testing, not just a scan
Scanners catch the easy issues. Auditors chain findings by hand to show which ones genuinely matter.
A CERT-In aligned method
We follow CERT-In and OWASP testing guidance, so the report holds up with regulators and with your customers' auditors.
Two reports from one audit
A technical findings register for engineers and a board summary for everyone else, rather than one document that suits neither.
Real client work, with the receipts
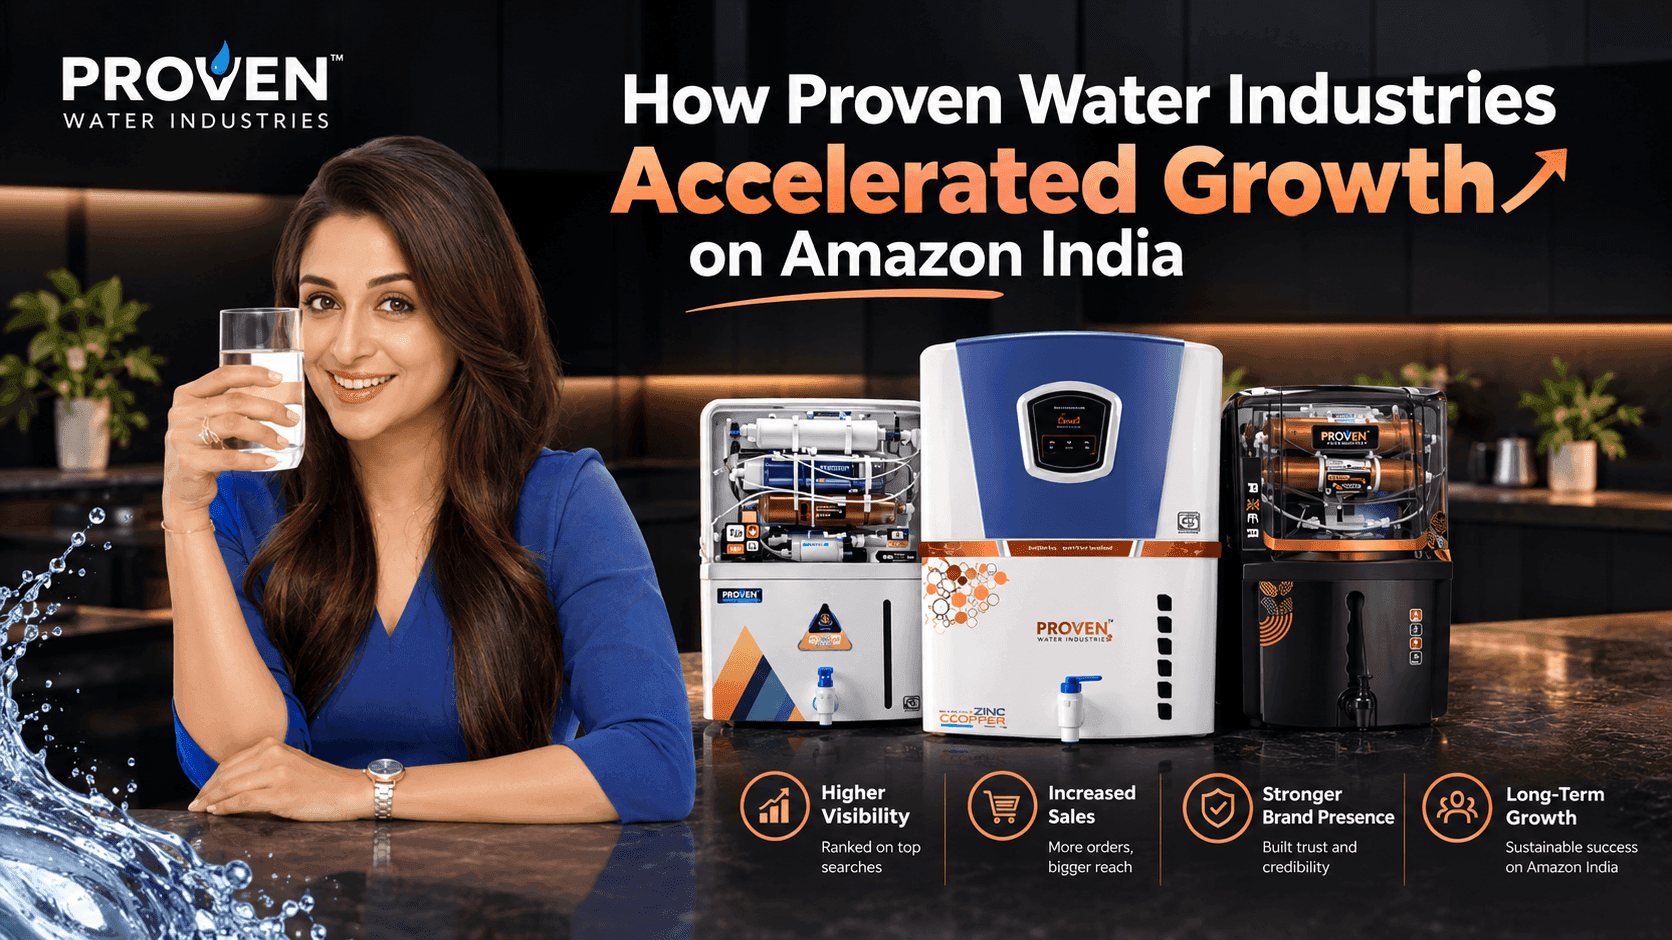
200%
Improvement in conversion performance
Proven Water Industries
Proven's growth on Amazon over the engagementDcrayon's work on Proven's Amazon account has run as a long-term growth programme rather...
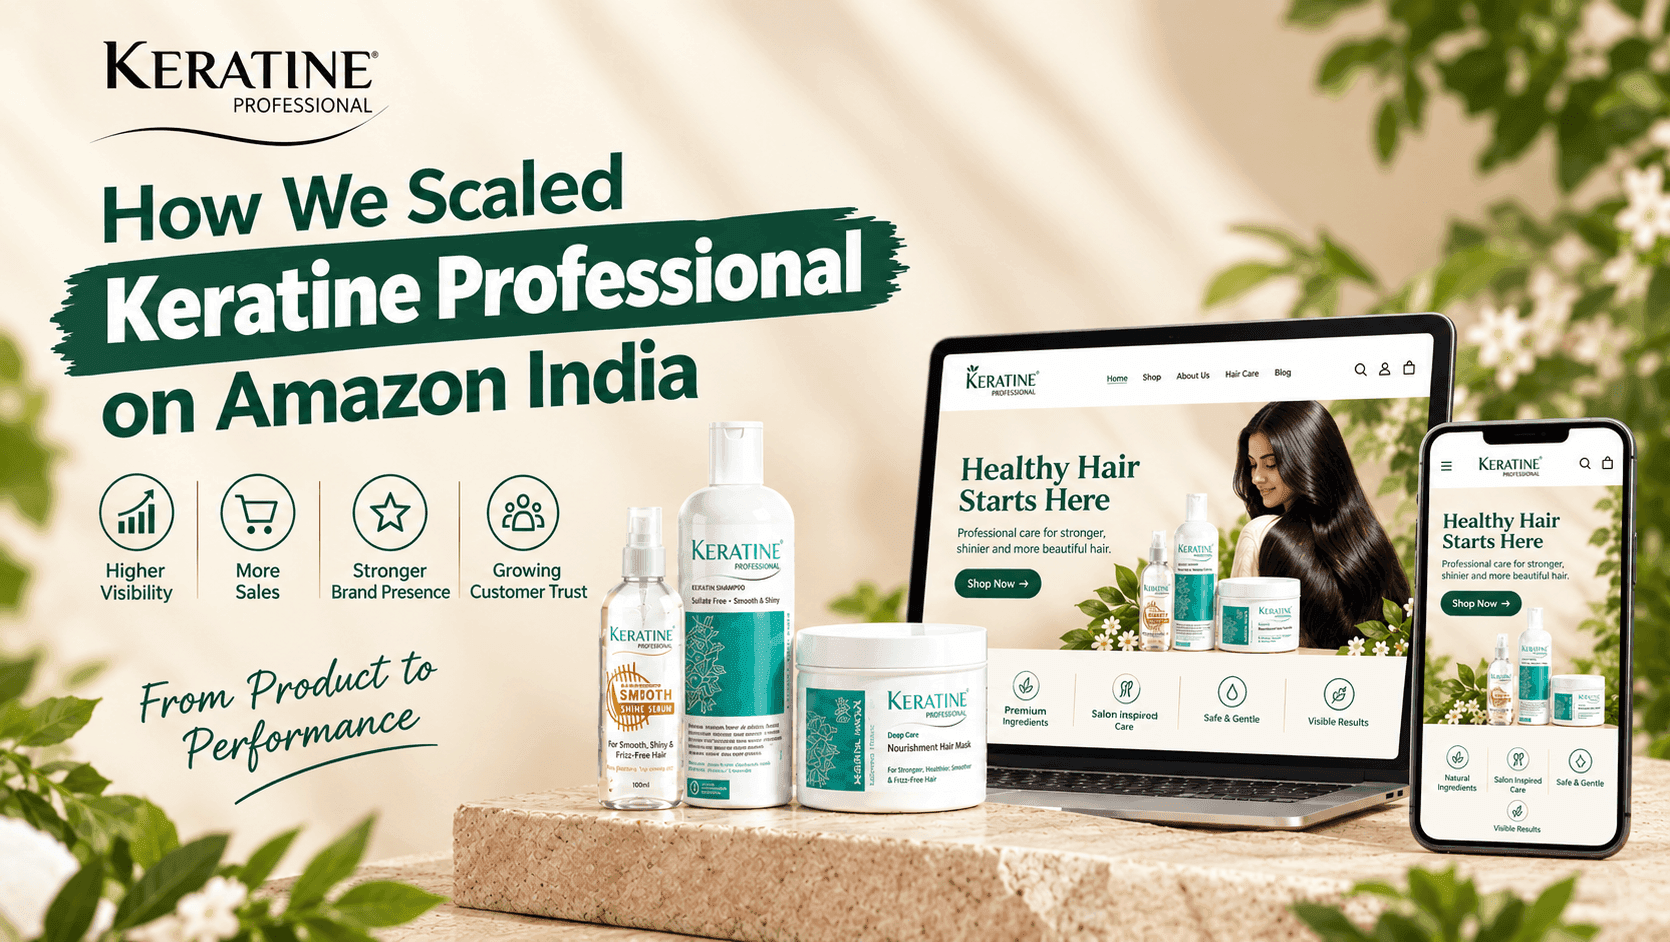
Keratine Professional
What is in place on Keratine Professional's accountOn Amazon.in today, the brand's lead listings name the product type, the hair concern...
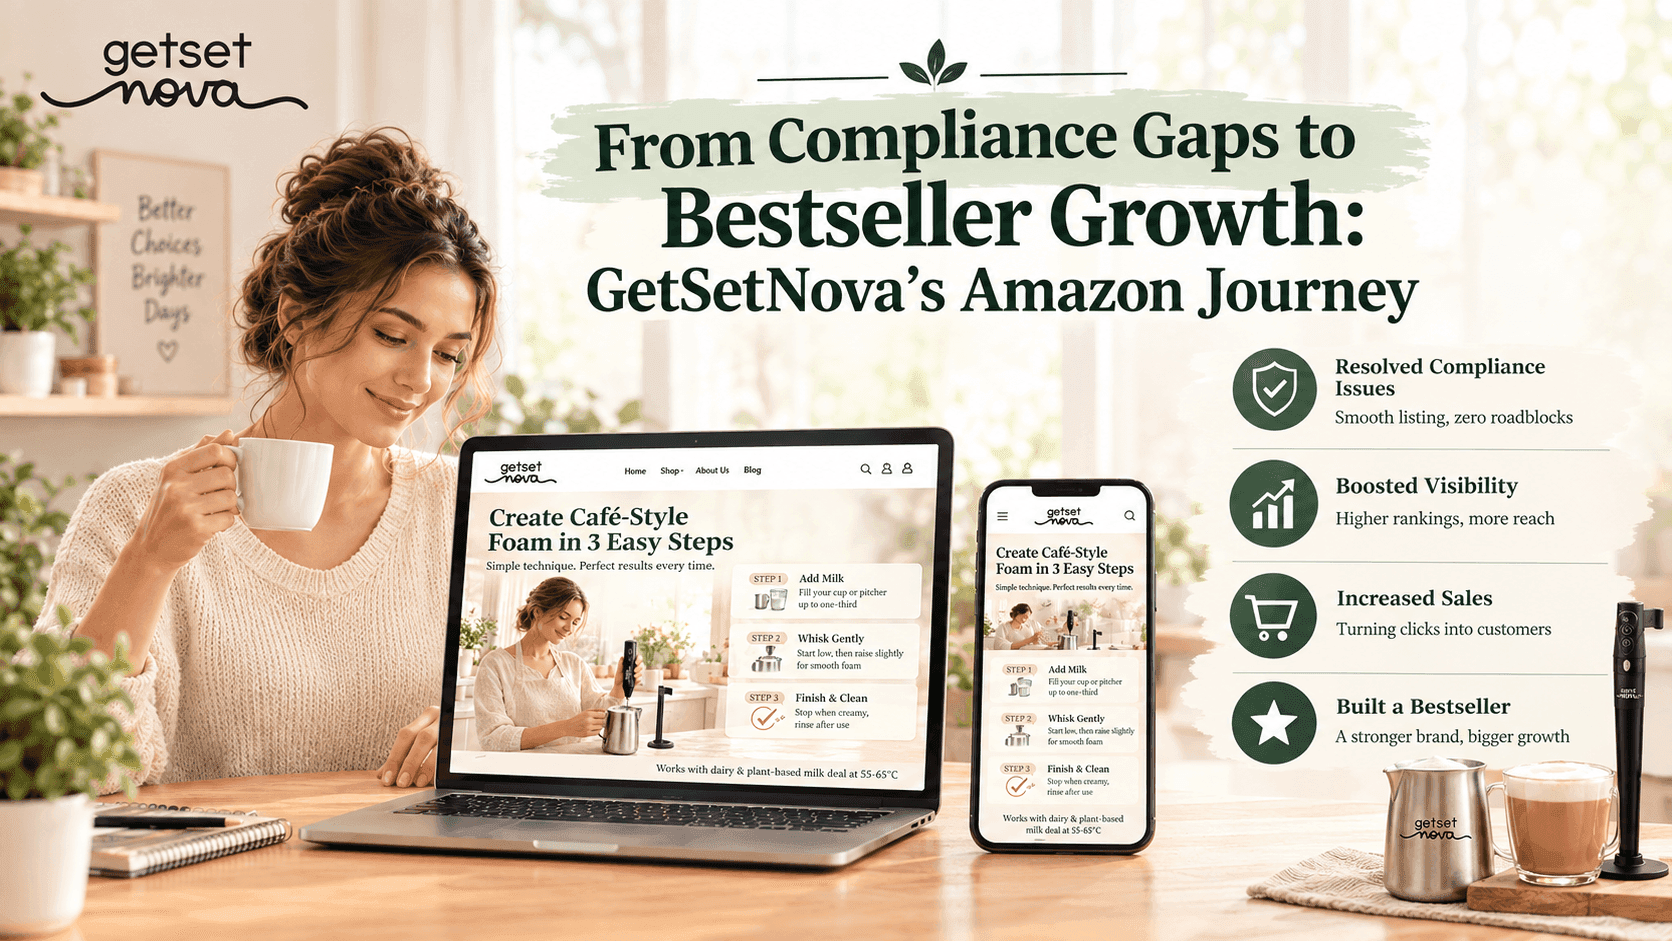
3,400%
Sales growth on Amazon India
GetSetNova
Sales up 3,400% on Amazon IndiaOver the engagement, GetSetNova's sales on Amazon India are up 3,400%, and the brand holds Amazon Best...
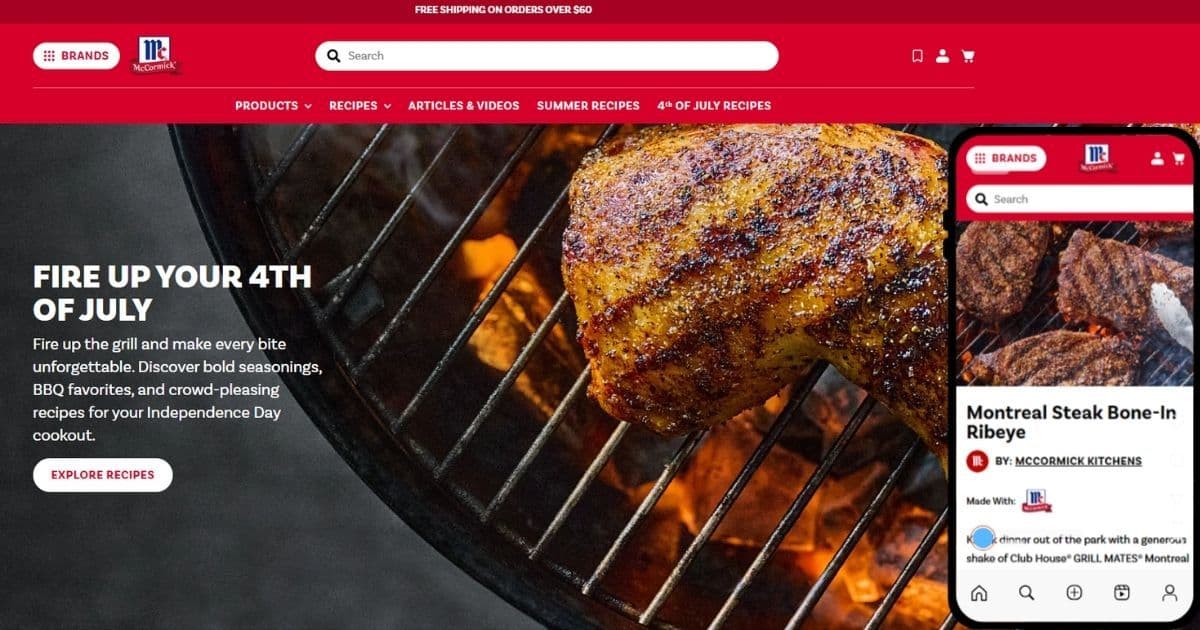
McCormick & Company
What changed on McCormick's front endThe front end now loads non-essential scripts after the main content, runs third-party tags through...
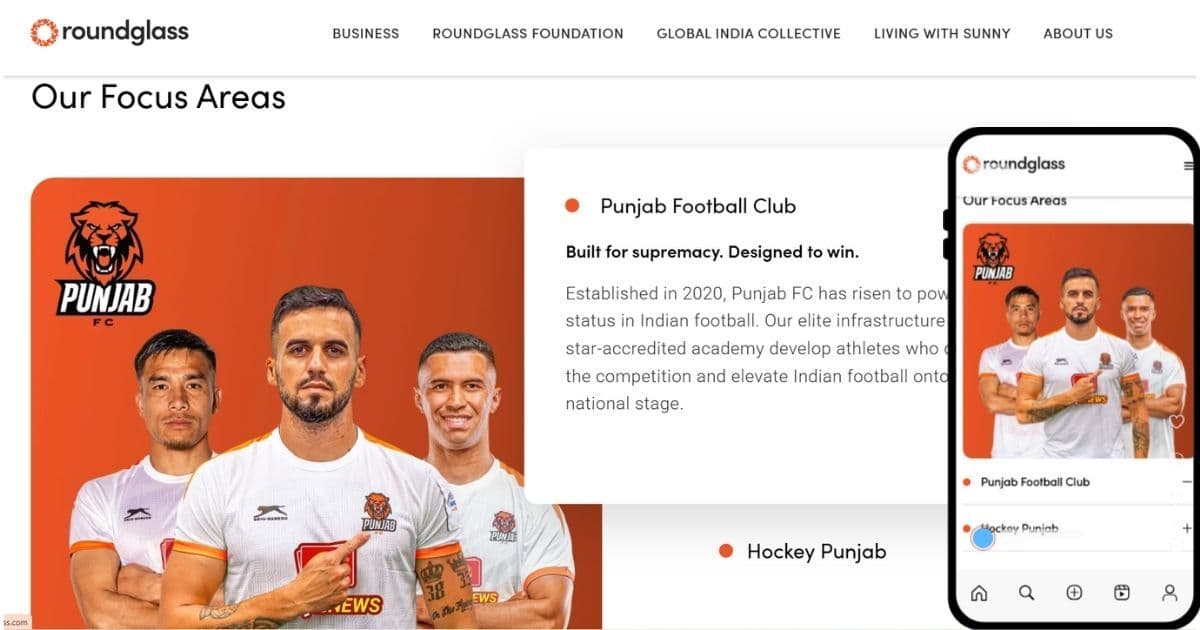
Roundglass
What changed for Roundglass's HR team, IT and new employeesAccount creation, group membership and licence assignment now follow the...
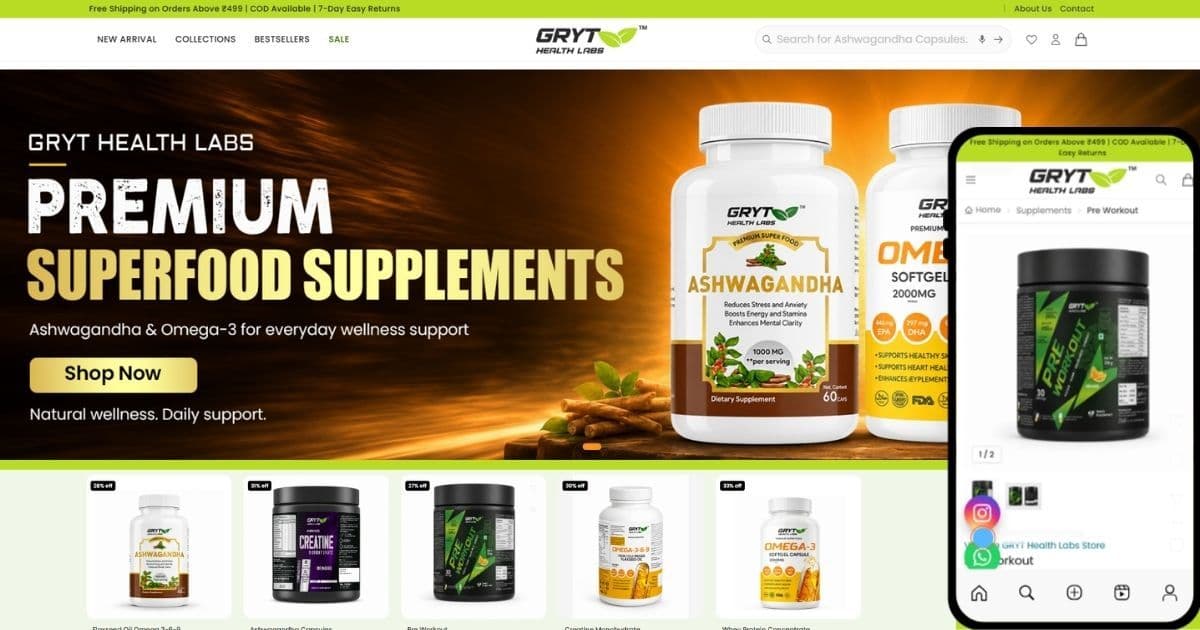
GRYT Health Labs
What GRYT shoppers can do on the storeShoppers can check the brand's licence and ownership details, compare single units with packs of...
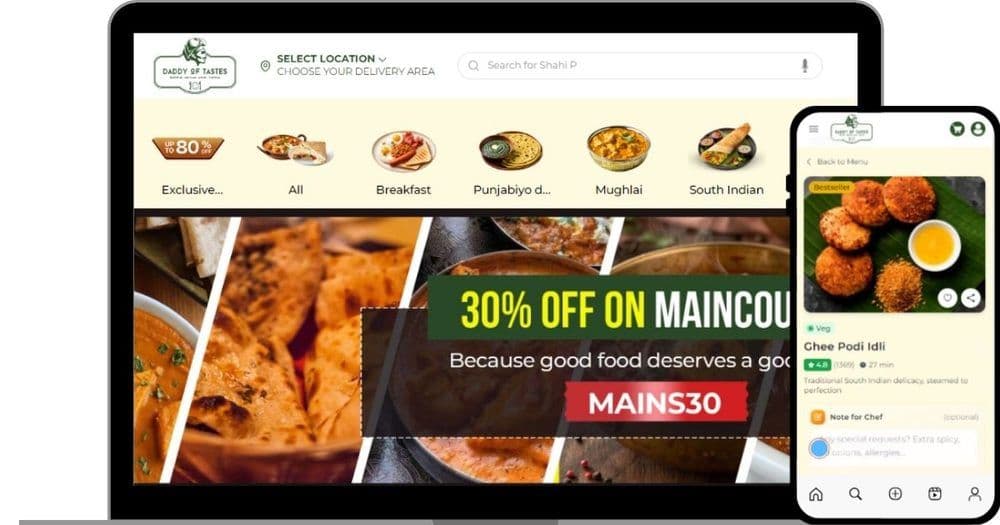
Daddy of Tastes
What the Daddy of Tastes kitchens and riders work withCustomers can order from the full menu, pin their exact location, pay through...
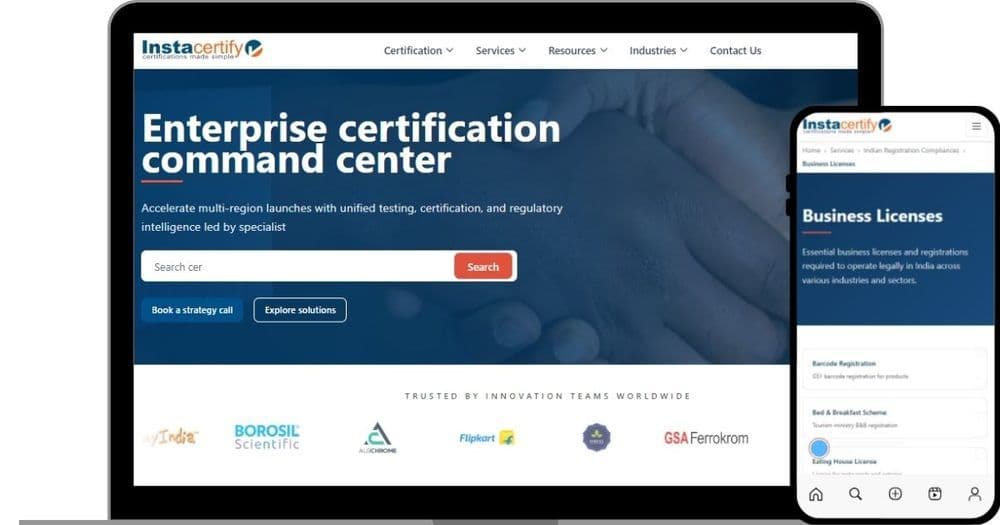
Instacertify
What Instacertify's visitors could doVisitors could search for a certification from the first screen, see two clear next steps, and move...
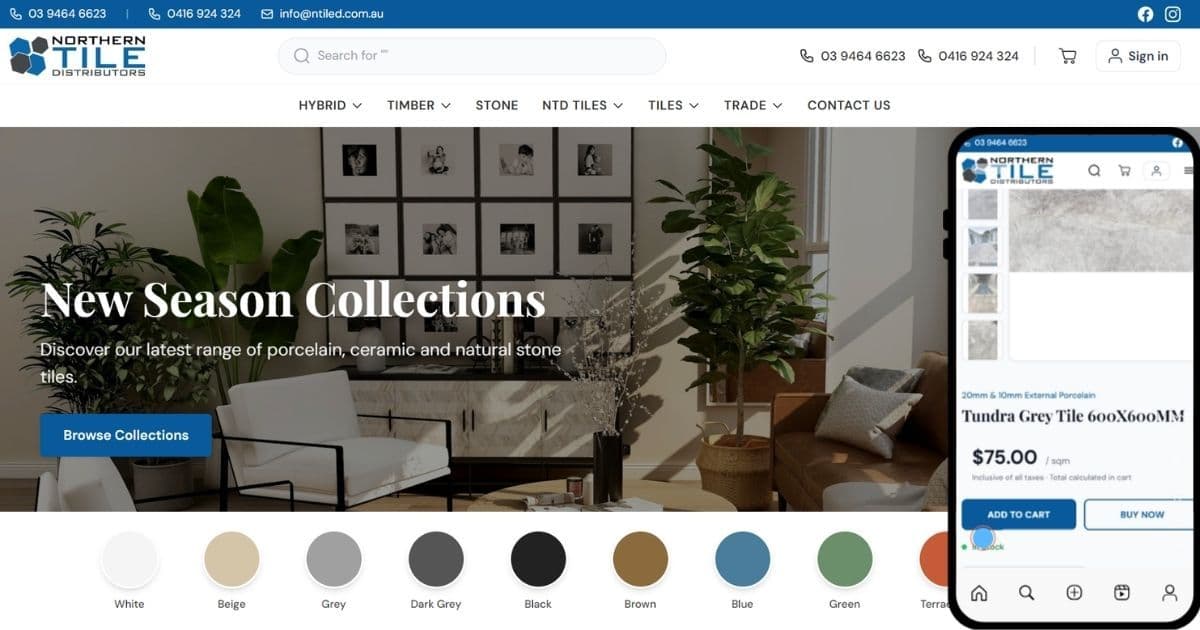
Northern Tile Distributors
The storefront delivers a clean shopping experience on both desktop and mobile. Page load times improved significantly, the add-to-cart rate...
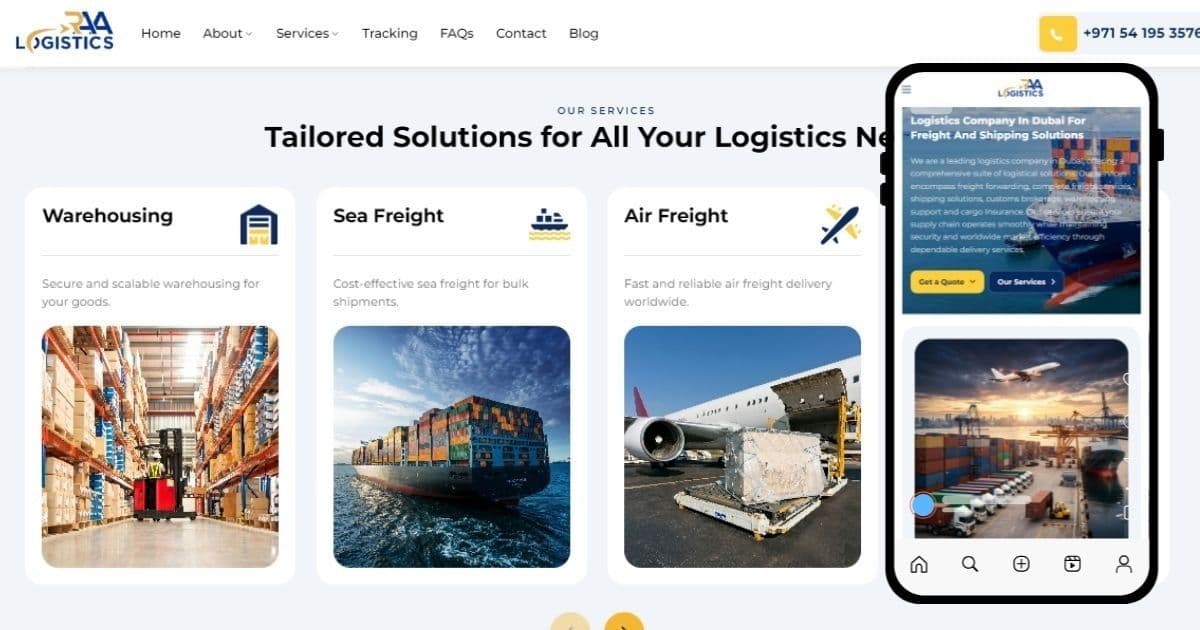
RAA Logistics
What RAA's customers and team have nowProspective customers can find the exact service they need, read what it covers, see who runs the...
The Risk Score costs nothing. The remediation plan is yours to keep.
Across our 60+ active solutions retainers, the median 12-month cost we measure for teams running without a structured security audit and compliance program lands in the Rs 6L to Rs 90L band. Book the scoping call to size yours.
A no-cost Dcrayon Risk Score across five security domains
A written remediation plan ranked by exploit risk
A mutual exit clause in every SoW, no annual lock-in
A senior auditor on the account from the first scoping call
Security Audit FAQs
It begins with a scoping call to agree the assets in range, the testing windows, and the rules of engagement. Post-incident work is scoped with priority and clear escalation.
Both. Some clients hand us the whole security audit and compliance function; others keep an internal team and use us as the senior architect and escalation point for penetration testing and remediation. We scope per account.
Most security audit engagements start at Rs 4 to 8 lakhs per month in India, or USD 6 to 15 thousand per month globally. One-off audits are scoped lower.
Yes. Every proposal call includes a no-cost Risk Score readout across five security domains. No follow-on commitment is required.
Ready to Grow Your Business?
Get expert digital marketing that delivers measurable results. Free consultation available.
We will review how your search, paid and marketplace channels are performing, and point out the gaps costing you the most right now.
You will finish the call knowing what to fix first, whether or not you work with us.