 All Case Studies
Our incident response retainer clients cut dwell time, not just alert noise metrics
Two recent incident response engagements, from first alert to lessons learned. Breach details stay under MNDA; a full walkthrough on your scoping call.
Cybersecurity and Compliance engagement,
Incident response and digital forensics lead
Dcrayon handled our breach like a drill they had rehearsed. They isolated the affected hosts, preserved forensic images with chain of custody, and gave us a containment timeline the board could follow.
Incident Response engagement: NIST 800-61 playbook, EDR host isolation, forensic imaging with documented chain of custody, and a post-incident review that closed the entry points attackers used.
Read Cybersecurity and Compliance engagement's Case StudyMid-market cybersecurity and compliance brand,
Incident response and detection lead
Our incident response plan was a PDF nobody had tested. Dcrayon ran a tabletop, rewrote the escalation playbooks, and had our team practiced before the next real alert landed.
Incident Response engagement paired with threat monitoring so alerts reached an on-call analyst. A tabletop exercise in the first week exposed the escalation gaps to fix first.
Read Mid-market cybersecurity and compliance brand's Case StudyWhy choose Dcrayon for Incident Response
Dcrayon has run 200+ solutions engagements for 60+ active retainers since 2016 from our Delhi HQ and Sheridan, Wyoming office. Our responders hold CEH, OSCP, and CISSP, and have handled breach containment and forensic triage across India, the US, the UK, and the UAE.
A named DFIR lead on every retainer
No rotating on-call pool. The forensics lead who learns your environment is the one who answers when an alert fires.
Readiness review before the first alert
A written response-readiness diagnostic and scope, so containment starts from a plan instead of a blank page in the middle of a live event.
AI-assisted forensics
We pair analyst judgment with tooling that timelines log data, clusters related alerts, and highlights lateral movement across the estate.
Reports your board can read
After every incident you get a plain-English report: what happened, how far it reached, what we contained, and what to fix, without the jargon.
HOW WE WORK
How Dcrayon works with the brands we partner with
A short film on how we work: the people you deal with, how we report, and the results we hold ourselves to.
What the retainer covers
Three phases of a live incident, and the work that happens before one starts.
Step 1: Containment
Stop the spread first Isolate affected hosts and accounts, cut the attacker's access, and keep the business running while the investigation starts.
Step 2: Disk and memory forensics
Preserve the evidence Images taken and handled so findings stand up later, with a timeline of what happened and how far the intruder reached.
Step 3: Notification and hardening
CERT-In and GDPR Regulatory notification support inside the deadlines, then closing the gap the attacker used so the same route does not reopen.
Response capabilities we bring to every incident
What comes standard on a Dcrayon incident retainer
Each capability below is run by the named DFIR lead assigned to your account, not handed to a rotating on-call queue.
Forensically sound evidence
Every action follows chain of custody: forensic disk images, memory captures, and a timestamped timeline that stands up for an auditor, a court, or a cyber-insurance claim.
AI-assisted threat hunting
Dcrayon AI correlates SIEM and EDR telemetry to surface indicators of compromise, map lateral movement, and flag persistence a manual sweep can miss.
Ransomware and extortion playbooks
Decision support for ransom demands, negotiation, and crypto-tracing partners, plus backup-recovery validation before payment is ever considered.
Regulatory notification support
We prepare the CERT-In six-hour report, the GDPR 72-hour breach notice, and the incident documentation your regulators and insurer will ask for.
Three frameworks behind every Dcrayon incident engagement
Assess, contain, harden. The readiness diagnostic, the containment playbook, and the DFIR toolkit we run on every incident.
Growth Intelligence (response-readiness axis)
A readiness review of your detection and response setup. We check EDR coverage, log retention, containment playbooks, CERT-In reporting readiness, and how fast your team can isolate a compromised host. Free on every proposal call.
Dcrayon Growth Engine (containment sequencing)
The step sequence that moves an incident from containment to eradication to recovery, with clear exit criteria at each stage before any system is reopened.
Dcrayon AI (DFIR toolkit)
Internal toolkit that parses logs at scale, timelines attacker activity, and drafts the prioritised hardening roadmap your remediation budget is built around.
How a Dcrayon incident retainer works
Three habits that make every response calmer than the last: rehearse, respond, review.
Step 1: Assess
A no-cost readiness review of how you would handle a live breach today. We map your detection coverage, log gaps, and containment steps, then hand you a prioritized fix list scored 0 to 100. No follow-on commitment.
Step 2: Contain
A written response plan built around a metric you pick, like mean time to contain. A senior DFIR lead owns the runbooks and playbooks. Month to month, no annual lock-in, and either side can end it at day 90.
Step 3: Harden
Weekly check-ins with your DFIR lead plus a plain monthly summary your finance team can read. The work builds on itself: tabletop drills sharpen detection, tuned alerts cut false positives, then SOAR playbooks automate first-line containment.
Get a breach readiness readout
A written review of how you would handle a live breach today, covering detection coverage and escalation paths.
Other Cybersecurity and Compliance solutions
Sibling Dcrayon services inside the Cybersecurity and Compliance category. Programs clients often layer alongside Incident Response.
WHY DCRAYON
Why teams put the retainer in place before they need it
Four commitments that decide how the first hour goes.
A named lead who knows your estate
No rotating on-call pool. The forensics lead who learns your environment in advance is the one who picks up the call.
Evidence handled so it holds
Imaging and chain of custody are done properly from the first hour, because containment that destroys evidence costs you later.
Readiness reviewed before the first alert
The retainer starts with a written readiness diagnostic, so containment begins from a known position rather than a cold start.
A report your board can read
After every incident: what happened, how far it reached, what was taken, and what changed. In plain English.
Real client work, with the receipts
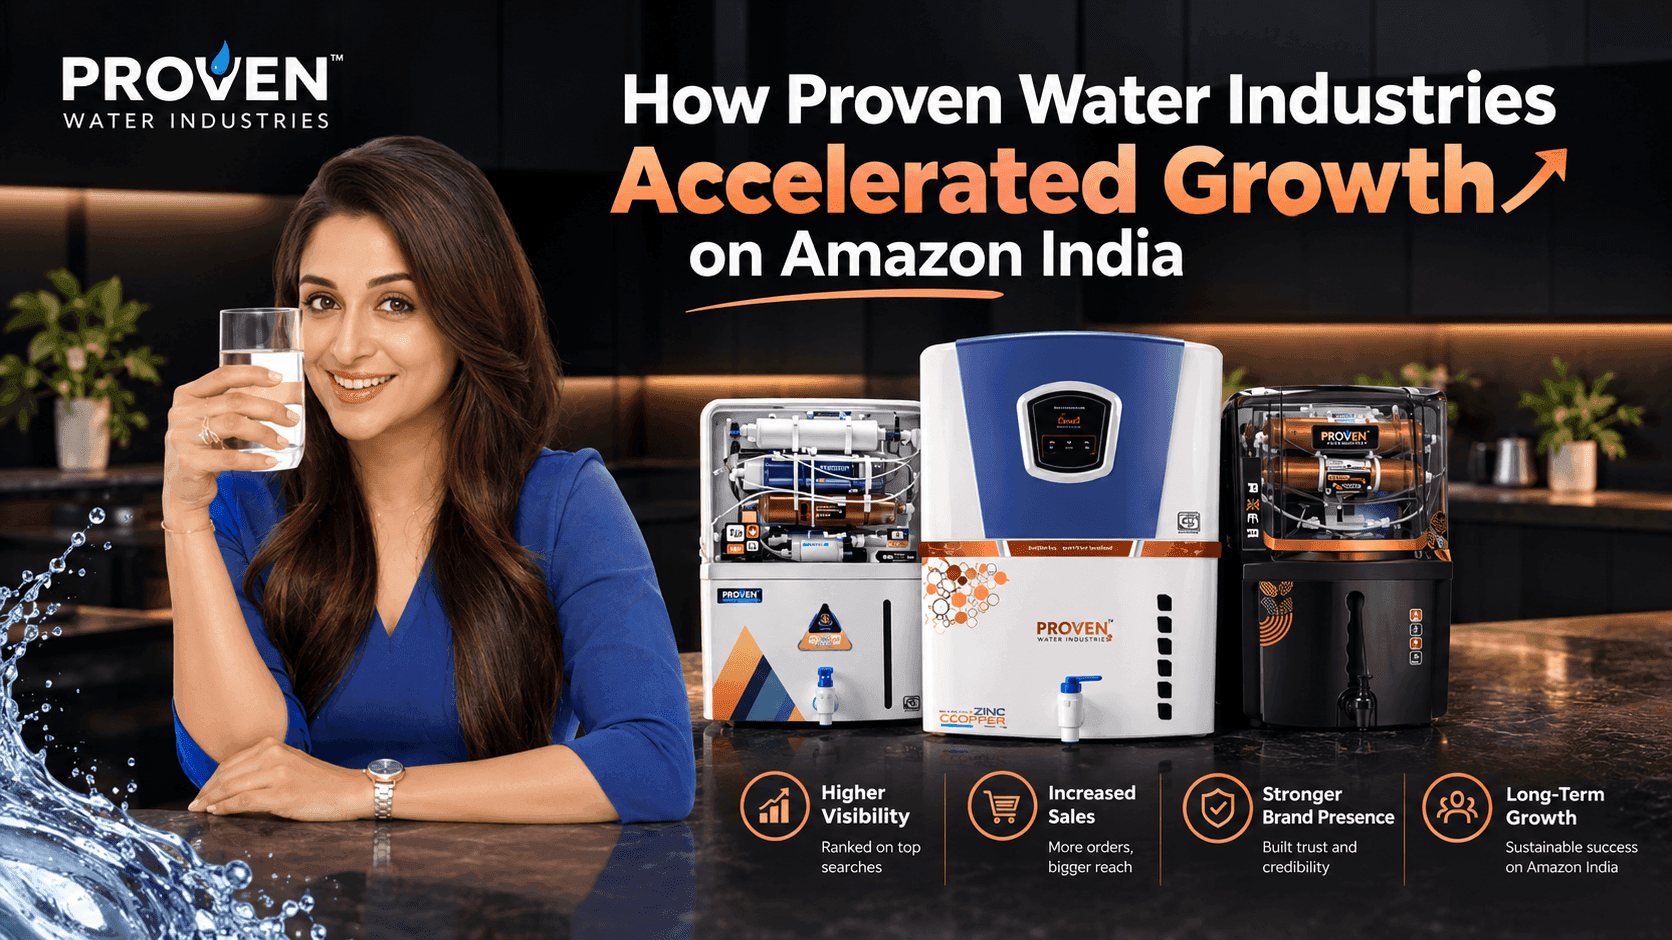
200%
Improvement in conversion performance
Proven Water Industries
Proven's growth on Amazon over the engagementDcrayon's work on Proven's Amazon account has run as a long-term growth programme rather...
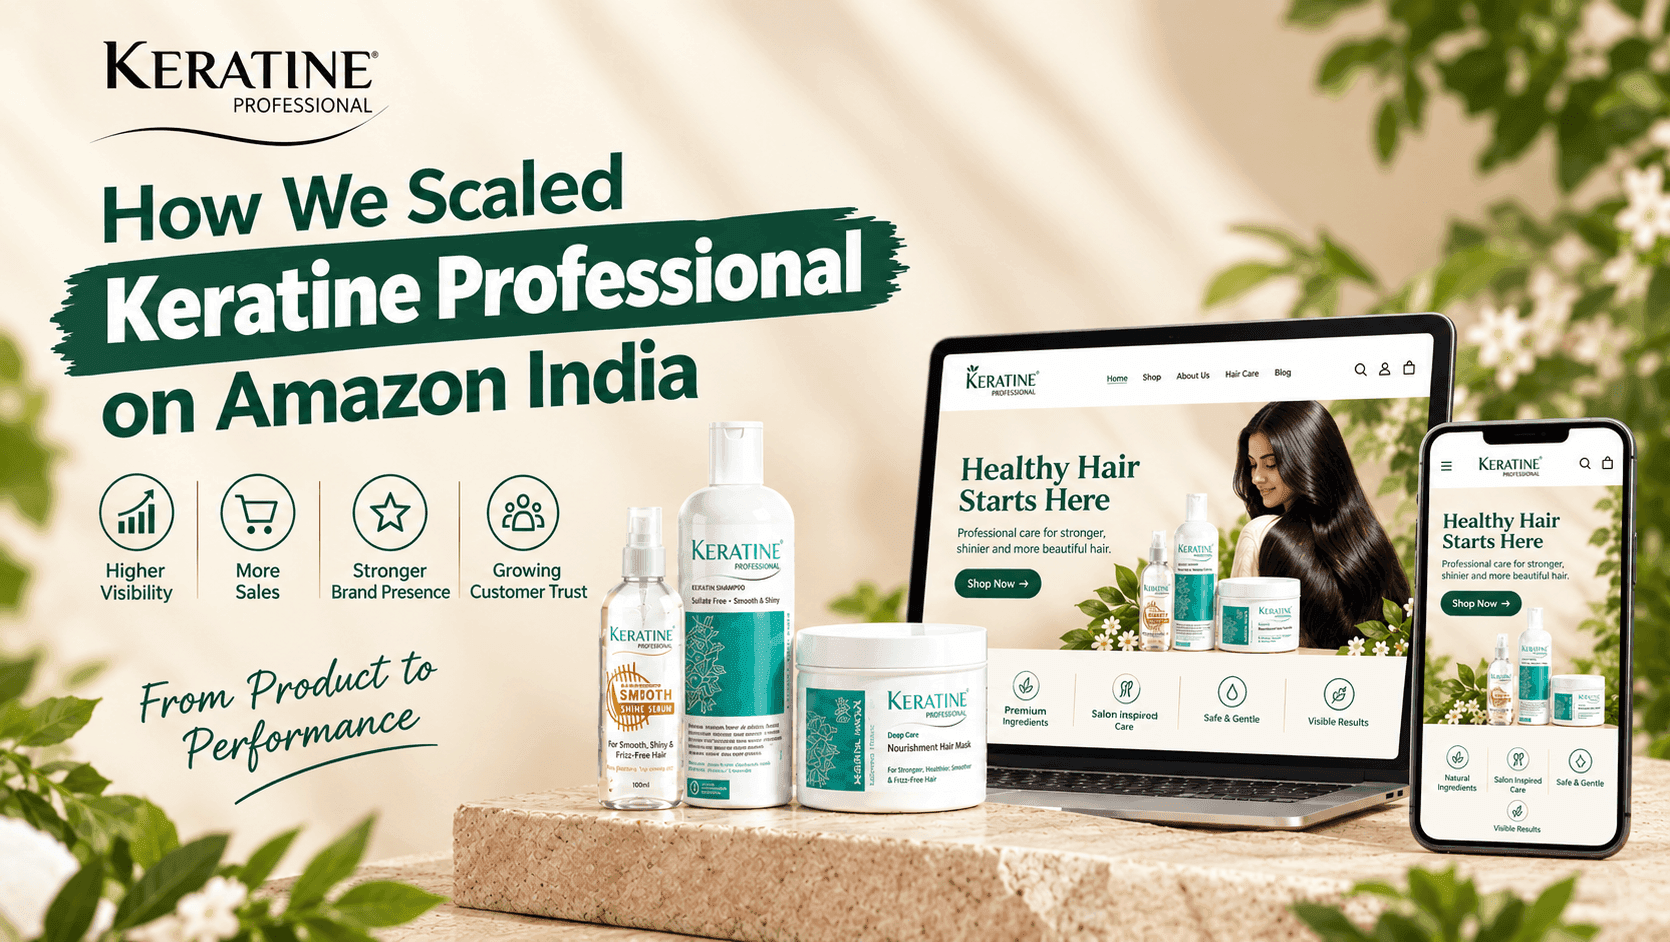
Keratine Professional
What is in place on Keratine Professional's accountOn Amazon.in today, the brand's lead listings name the product type, the hair concern...
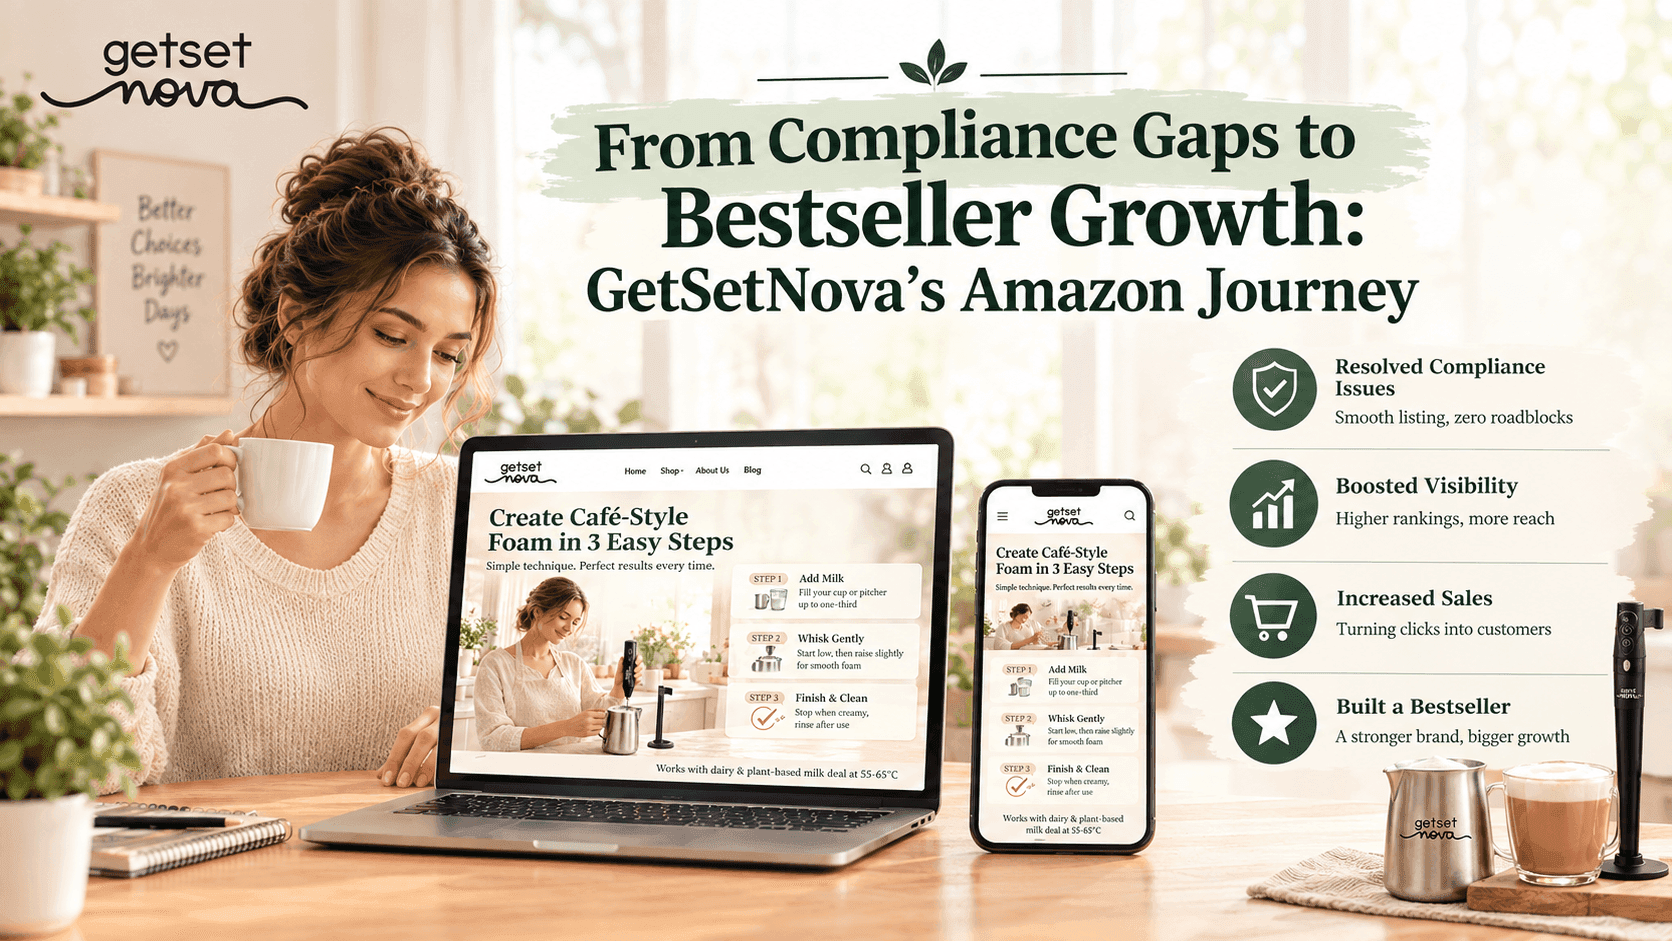
3,400%
Sales growth on Amazon India
GetSetNova
Sales up 3,400% on Amazon IndiaOver the engagement, GetSetNova's sales on Amazon India are up 3,400%, and the brand holds Amazon Best...
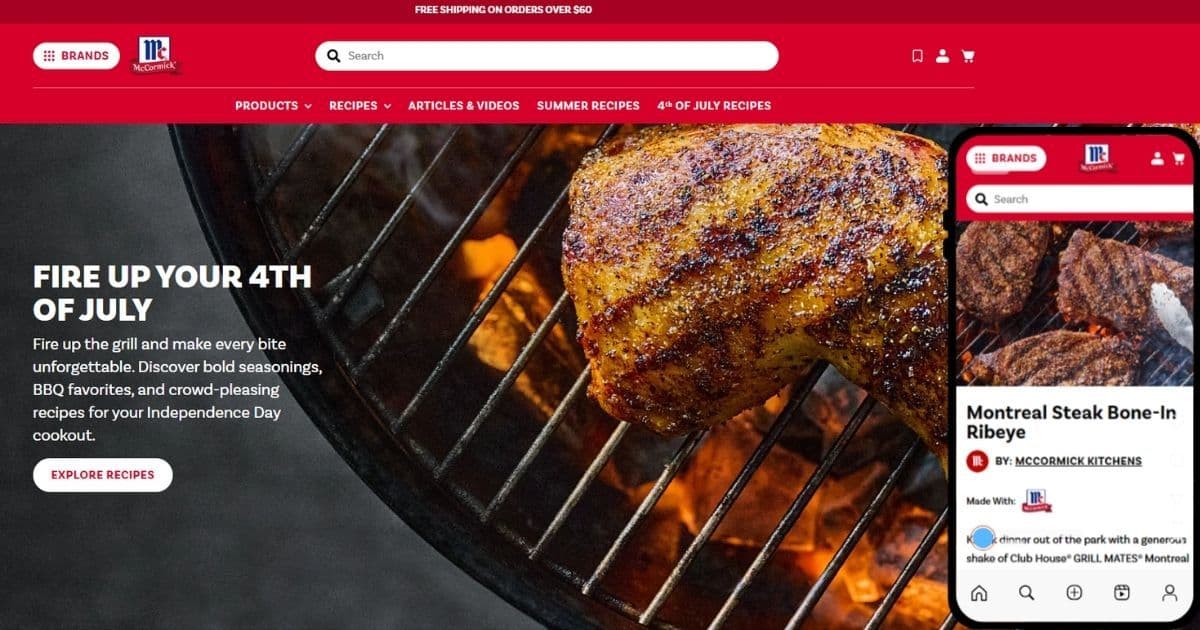
McCormick & Company
What changed on McCormick's front endThe front end now loads non-essential scripts after the main content, runs third-party tags through...
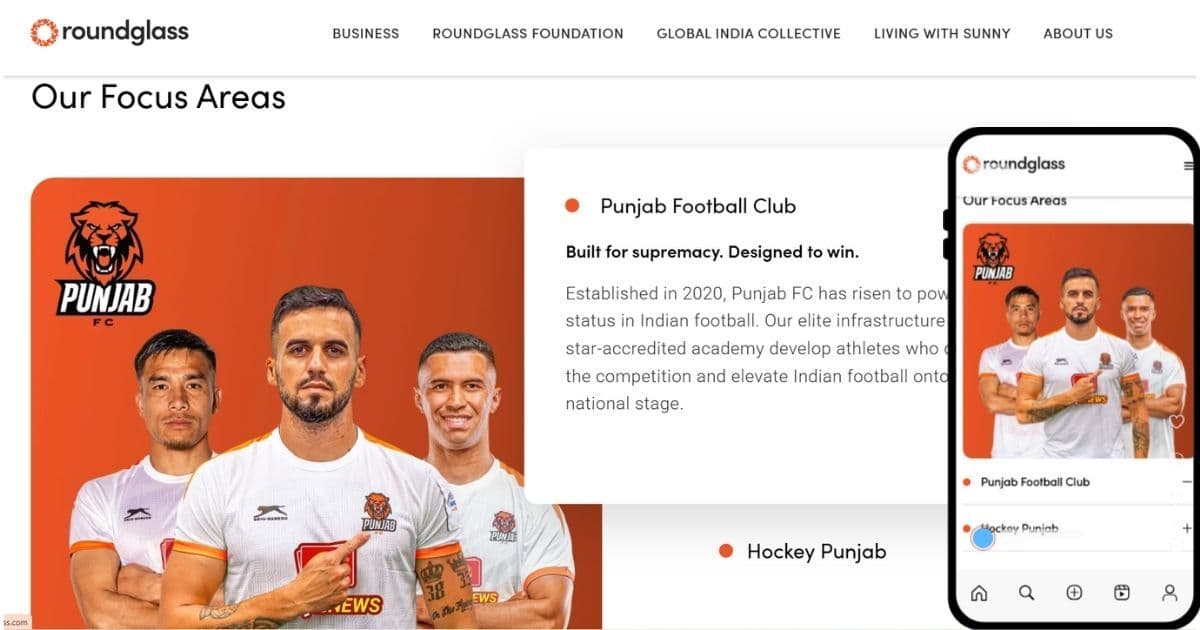
Roundglass
What changed for Roundglass's HR team, IT and new employeesAccount creation, group membership and licence assignment now follow the...
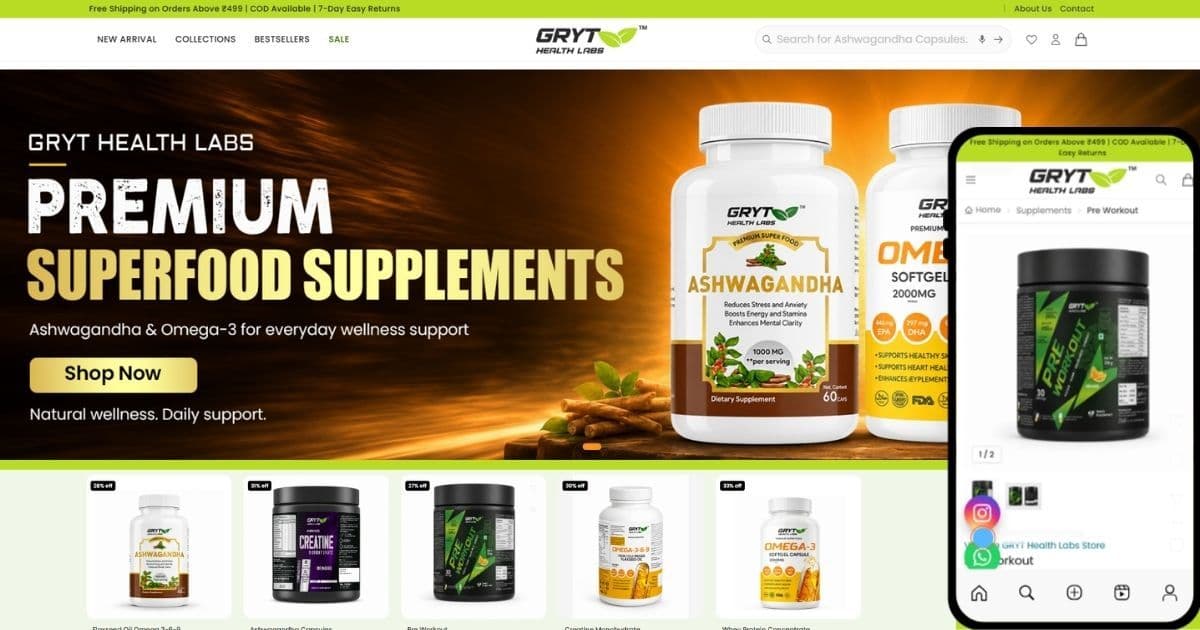
GRYT Health Labs
What GRYT shoppers can do on the storeShoppers can check the brand's licence and ownership details, compare single units with packs of...
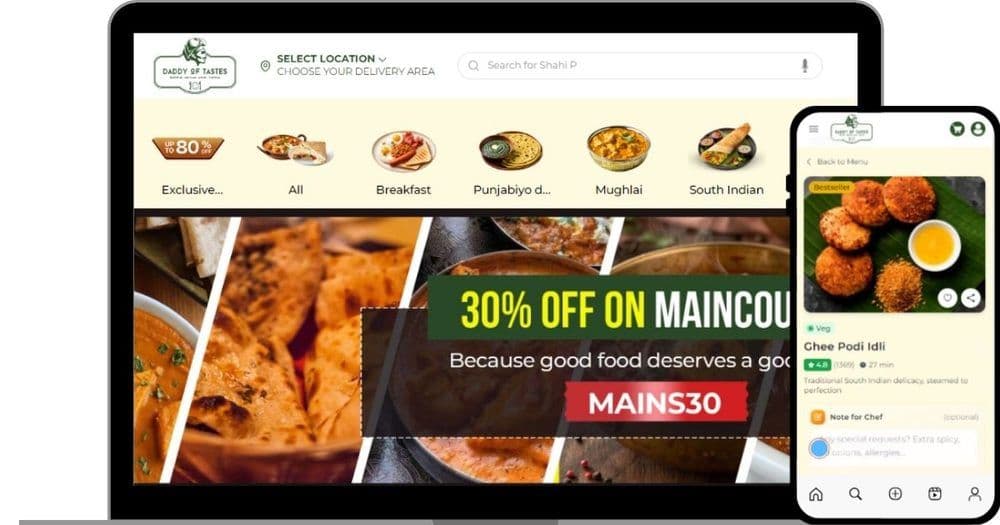
Daddy of Tastes
What the Daddy of Tastes kitchens and riders work withCustomers can order from the full menu, pin their exact location, pay through...
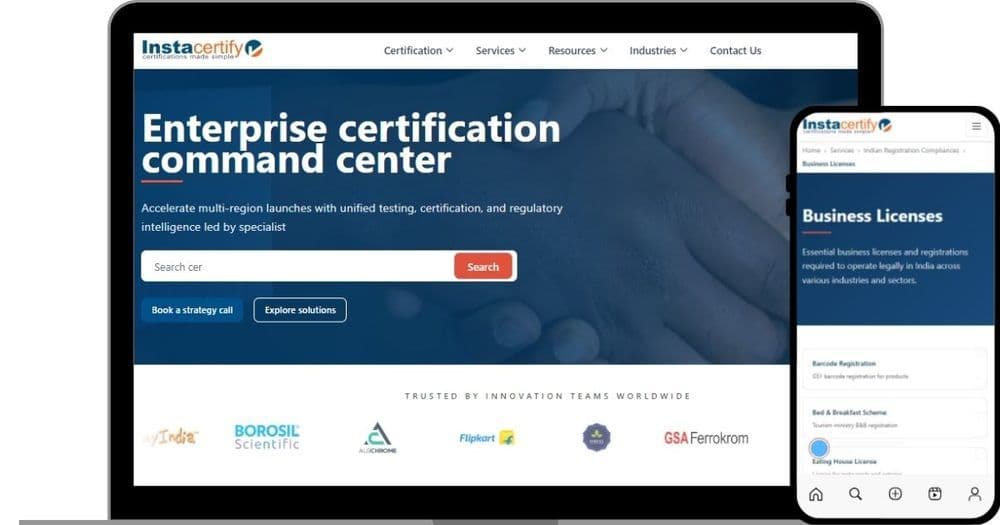
Instacertify
What Instacertify's visitors could doVisitors could search for a certification from the first screen, see two clear next steps, and move...
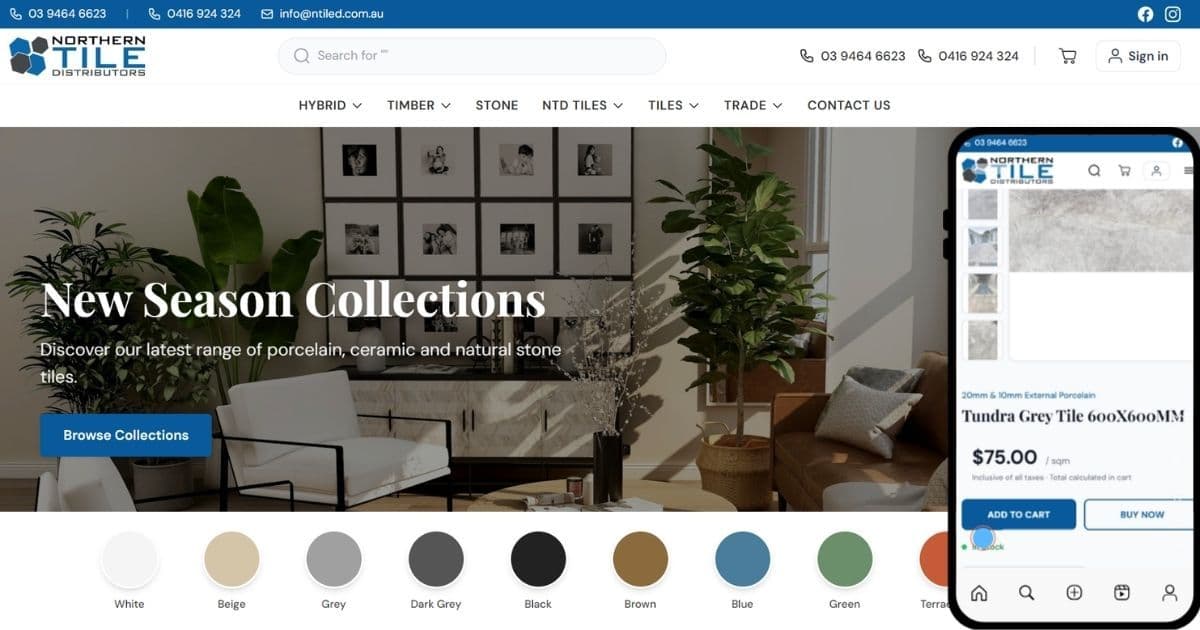
Northern Tile Distributors
The storefront delivers a clean shopping experience on both desktop and mobile. Page load times improved significantly, the add-to-cart rate...
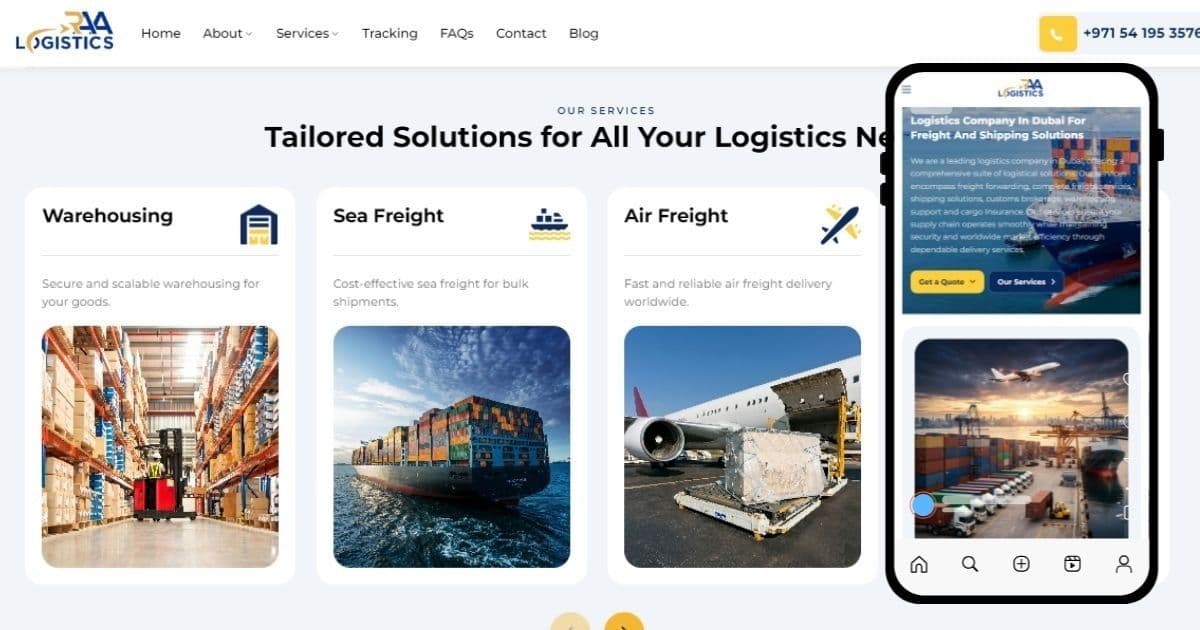
RAA Logistics
What RAA's customers and team have nowProspective customers can find the exact service they need, read what it covers, see who runs the...
The readiness review is free. The response plan is yours to keep.
Across our 60+ active solutions retainers, the 12-month cost we measure for teams with no incident response plan, counting downtime, breach cleanup, and lost data, lands in the Rs 6L to Rs 90L band. Book the scoping call to size yours.
No-cost response-readiness review scoring your detection and recovery gaps
Written response plan and runbooks tuned to your environment
On-call or full-retainer options, no annual lock-in
A named forensics lead on the account from the first call
Incident Response FAQs
Onboarding maps your systems, sets escalation contacts, and arranges log and EDR access, so when an alert fires we act from a known baseline rather than a cold start.
Both. Some clients keep us as their full incident response company; others keep us on retainer as the senior escalation their internal SOC calls the moment a breach hits. We scope per account.
Most retainers start at Rs 4 to 8 lakhs per month in India, or USD 6 to 15 thousand per month globally. Readiness reviews and tabletop-only engagements start lower.
Yes. Every proposal call includes a no-cost response-readiness review with a single score and your top gaps. No follow-on commitment required.
Ready to Grow Your Business?
Get expert digital marketing that delivers measurable results. Free consultation available.
We will review how your search, paid and marketplace channels are performing, and point out the gaps costing you the most right now.
You will finish the call knowing what to fix first, whether or not you work with us.