 All Case Studies
Clients with a defensible ROPA answer DSARs and pass audits metrics
Two recent data privacy engagements. Records of processing, DPIAs, and DLP coverage shared under MNDA on a scoping call.
Cybersecurity and Compliance engagement,
Data privacy and GDPR compliance program
Dcrayon mapped every data flow, built our Article 30 record, and set retention rules our legal team signed off on. DSAR responses now follow one documented process.
Data protection strategy: data mapping, a DPIA on high-risk processing, DLP policy in Microsoft Purview, and a consent and retention schedule reviewed with counsel.
Read Cybersecurity and Compliance engagement's Case StudyMid-market cybersecurity and compliance brand,
Privacy program with security review
We had no record of where personal data lived. Dcrayon delivered a full data inventory and a breach notification runbook that maps to the 72-hour rule.
Data protection work alongside a wider cybersecurity review. A gap assessment against GDPR and PCI DSS set the baseline for the privacy roadmap.
Read Mid-market cybersecurity and compliance brand's Case StudyWhy choose Dcrayon for Data Protection Strategy
Dcrayon has shipped 200+ solutions engagements for 60+ active retainers since 2016 from Delhi HQ and Sheridan, Wyoming. AWS + Azure + GCP-certified architects, CEH + OSCP + CISSP on staff. AI-first since the 2024 pivot.
A named security architect on every account
No trainees practicing on your regulated data. The GDPR consultant who scopes your program stays on it through delivery.
A five-axis data protection Score up front
A written diagnostic and a fixed estimate up front, so you see scope and cost before any contract, not after a long discovery phase.
AI-assisted monitoring since 2024
Every engagement includes AI-assisted work by default: anomaly detection on data access, exfiltration alerts, and policy-drift monitoring across endpoints.
A monthly readout in plain numbers
A weekly working cadence and a monthly Score tied to one privacy or security metric. A report your CFO and data protection officer can read without translation.
HOW WE WORK
How Dcrayon works with the brands we partner with
A short film on how we work: the people you deal with, how we report, and the results we hold ourselves to.
What a data protection programme covers
Three workstreams that take regulated data from unmapped to audit-ready.
Step 1: Classification and data mapping
Know what you hold Personal and cardholder data inventoried across your stack, with records of processing that match how the systems actually behave.
Step 2: Encryption and key management
At rest and in transit AES-256 at rest, TLS in transit, and a key rotation schedule that someone owns, mapped to ISO 27001 and SOC 2 controls.
Step 3: Loss prevention and immutable backups
Containment and recovery Loss-prevention policies tuned to your real data flows, plus immutable backups tested by restoring them.
Technical controls we build into every data protection strategy
What every Dcrayon data protection strategy engagement includes by default
Each control below maps to a measurable factor in your data privacy posture, built and verified by the GDPR consultant on your account.
Audit-ready evidence
Every control change ships with audit evidence: a records-of-processing update, before and after risk rating, DPIA notes, and a runbook entry for assessors.
Continuous data monitoring
DcrayonAI watches for unusual data access, flags exfiltration patterns, and alerts on policy drift across your storage, databases, and endpoints from day one.
Retention and disposal discipline
Retention schedules and disposal automation stop needless storage of personal data.
You see records held, minimized, and deleted, not just storage spend.
Compliance control mapping
Every change maps to a named control under GDPR, PCI DSS, ISO 27001, and SOC2, so evidence is ready when a data privacy audit lands.
Three tools we run on every data protection strategy engagement
Score, Plan, Compound. A privacy and security diagnostic, a 90-day control roadmap, and the toolkit we run on every data protection strategy engagement.
Growth Intelligence (data protection axis)
A data-mapping and gap assessment against GDPR Articles 30 and 32, the DPDP Act, and PCI DSS. We chart where personal and cardholder data lives, who touches it, and which controls are missing. Free on every proposal call.
Dcrayon Control Roadmap (data protection sequencing)
A 90-day roadmap that sequences data protection work back to one privacy or security metric you pick, so gaps close in priority order inside a quarter.
DcrayonAI (data protection toolkit)
An internal toolkit that runs data mapping and DLP audits, then generates a prioritized remediation list your CFO and data protection officer can budget.
How Dcrayon runs a data protection strategy
Three repeatable practices that harden data protection across cycles.
Step 1: Score
Free Growth Intelligence readout in one business day. We inventory your personal and cardholder data flows, check lawful basis and cross-border transfer paths, and score your data loss prevention coverage, then give one 0-100 number plus the gap list. No follow-on commitment.
Step 2: Plan
Written 90-day data protection plan tied to one control gap you pick, from records of processing to encryption at rest. A CIPP-certified GDPR consultant writes the controls, and either side can close the SoW. No annual lock-in.
Step 3: Compound
Weekly working session with your lead consultant plus a monthly board-ready summary. The programme builds in order: data mapping in cycle one sets the DLP rules in cycle two, which feed audit-ready evidence in cycle three.
Get a data protection readout
A written inventory of your regulated data flows and control gaps, with a fixed estimate, in one business day.
Other Cybersecurity and Compliance solutions
Sibling Dcrayon services inside the Cybersecurity and Compliance category. Programs clients often layer alongside Data Protection Strategy.
WHY DCRAYON
Why regulated teams run this programme with us
Four commitments that hold up in front of an auditor.
Controls mapped to named clauses
Every gap is tied to a specific GDPR, PCI DSS or ISO 27001 control, so remediation survives the audit conversation.
A named consultant on regulated data
No trainees practicing on personal data. The consultant who scopes the programme is the one who runs it.
Backups are restore-tested
Immutability is verified by restoring, because a backup nobody has recovered from is an assumption, not a control.
A board-ready summary each month
One page tying open gaps to risk and cost, written for a board rather than for a control framework.
Real client work, with the receipts
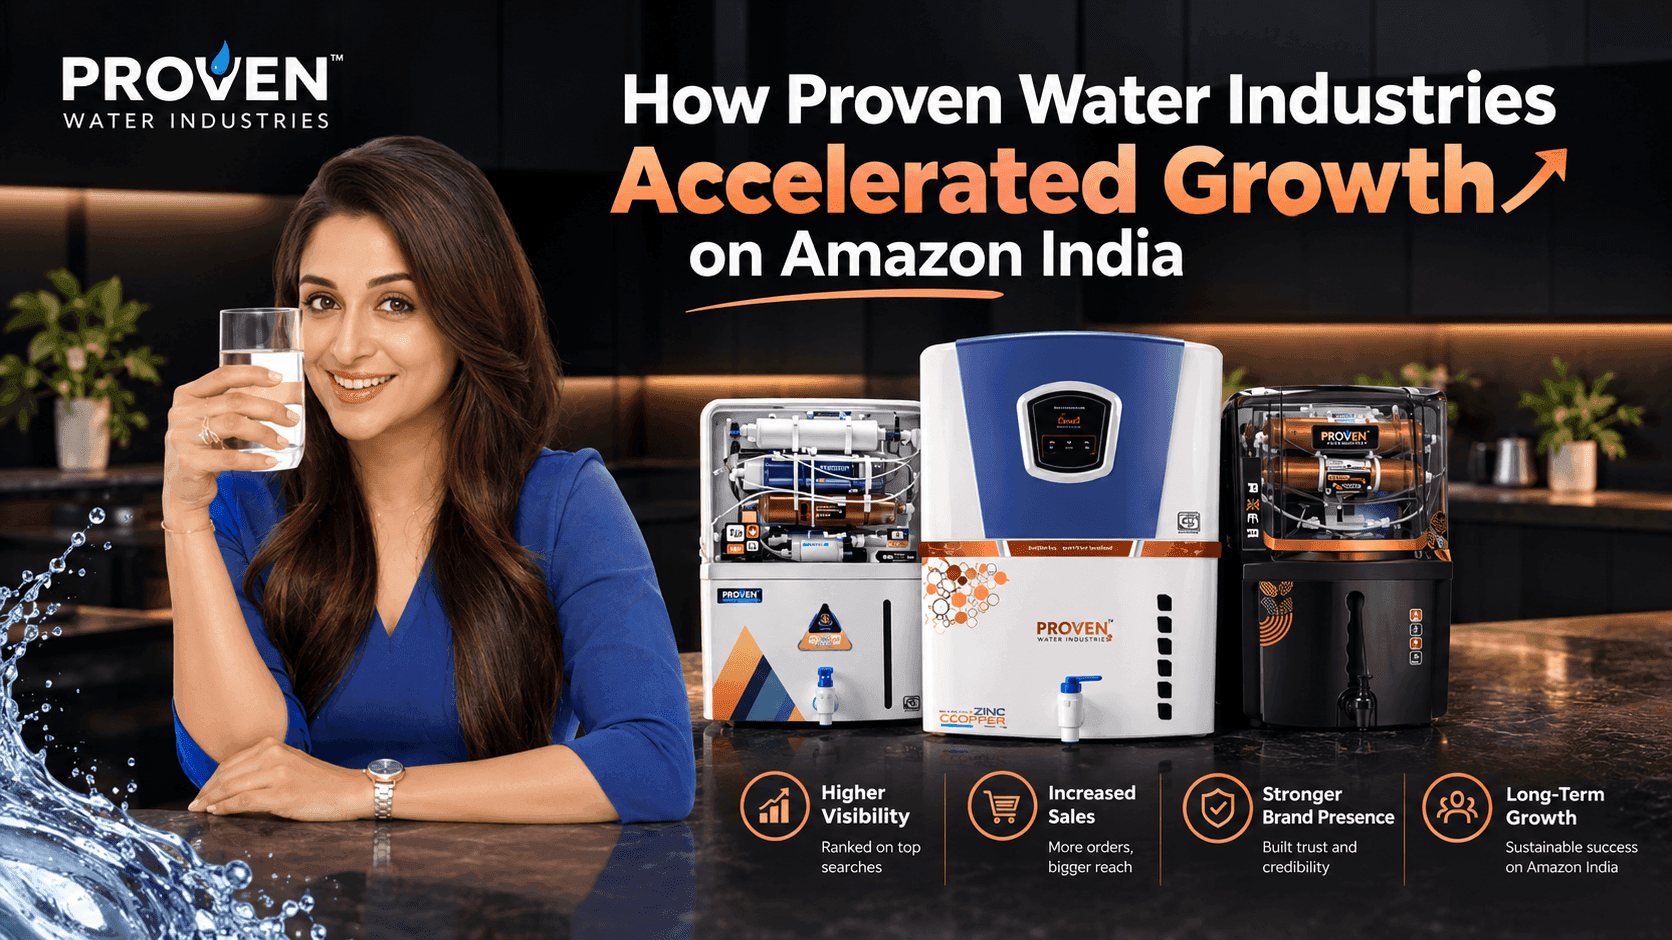
200%
Improvement in conversion performance
Proven Water Industries
Proven's growth on Amazon over the engagementDcrayon's work on Proven's Amazon account has run as a long-term growth programme rather...
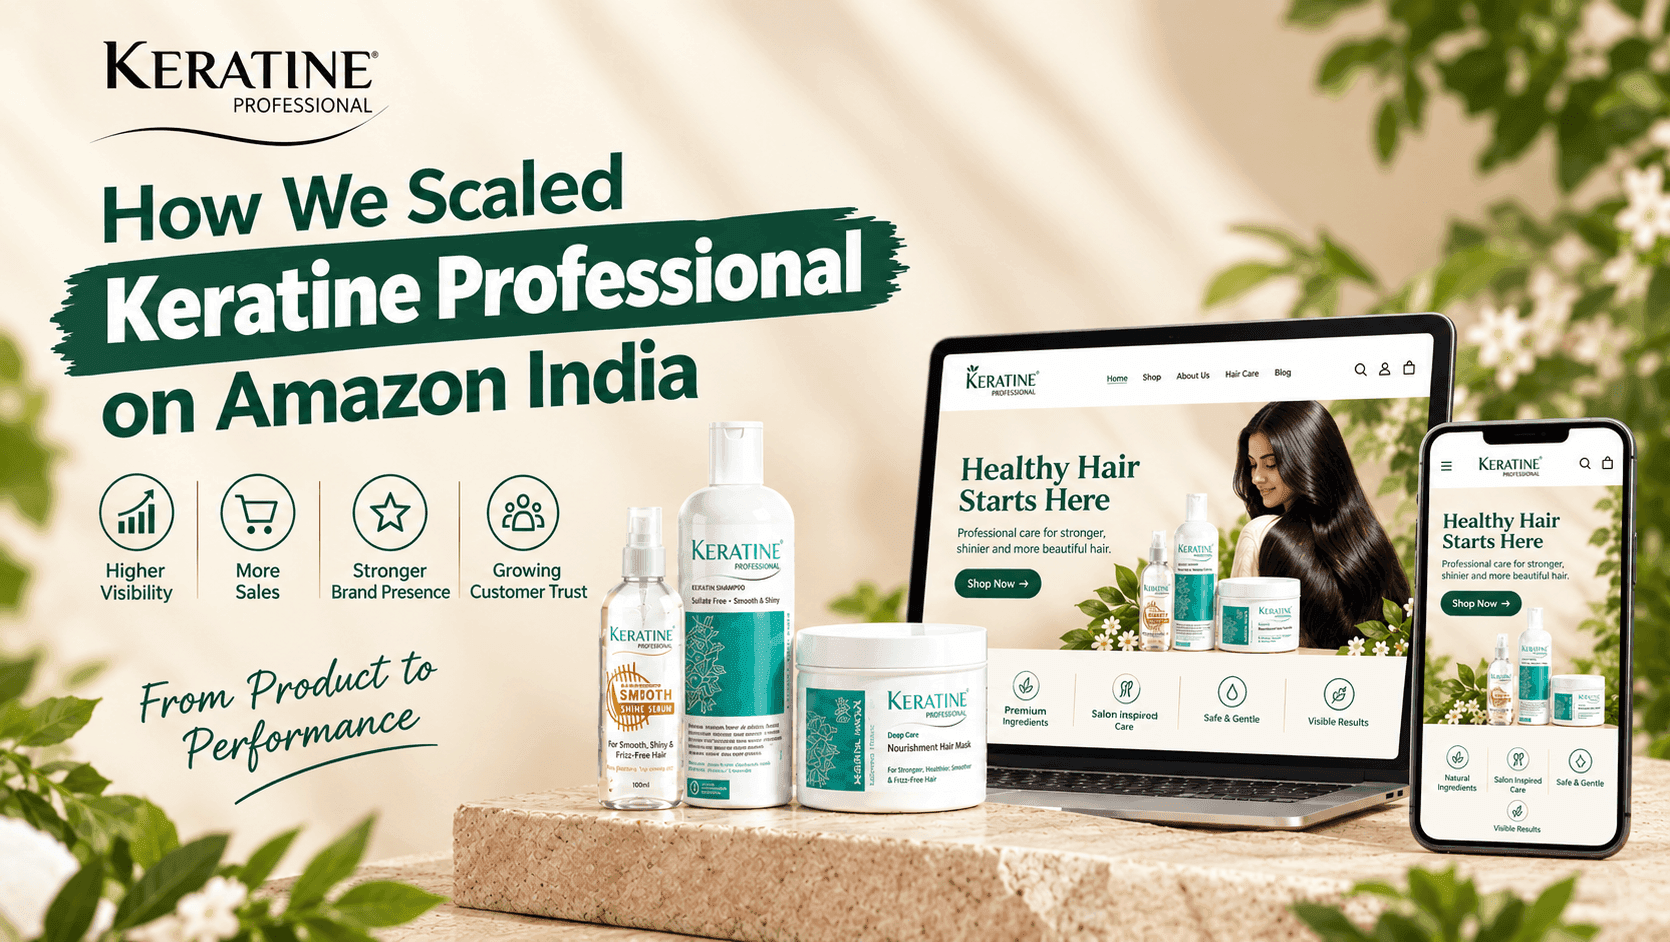
Keratine Professional
What is in place on Keratine Professional's accountOn Amazon.in today, the brand's lead listings name the product type, the hair concern...
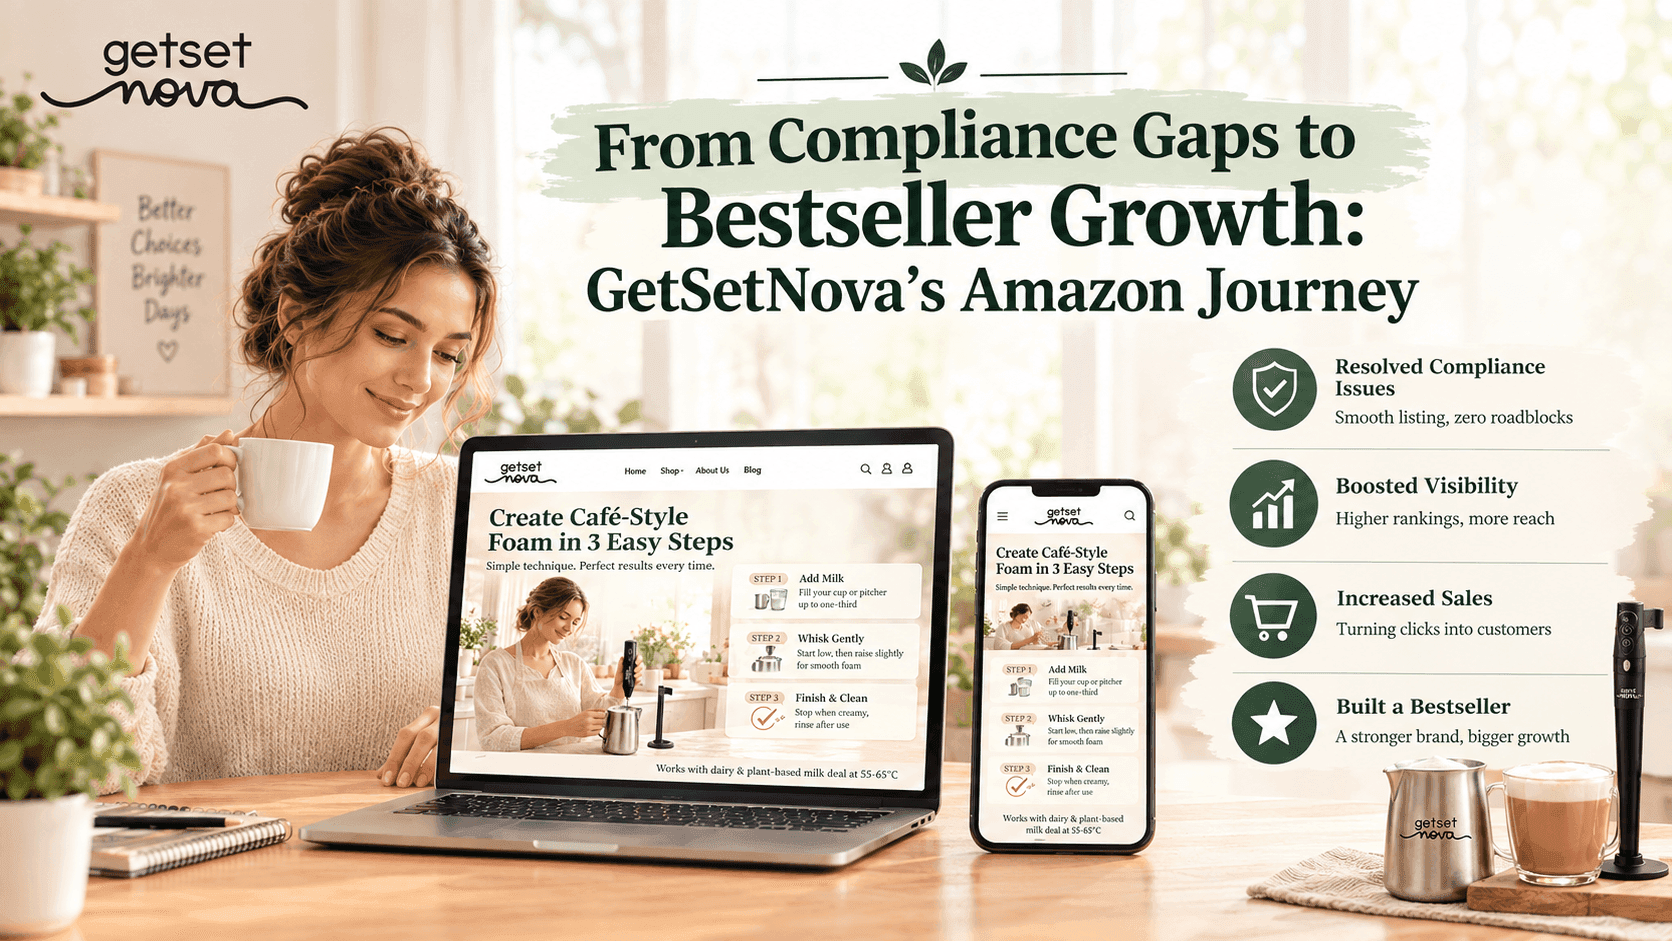
3,400%
Sales growth on Amazon India
GetSetNova
Sales up 3,400% on Amazon IndiaOver the engagement, GetSetNova's sales on Amazon India are up 3,400%, and the brand holds Amazon Best...
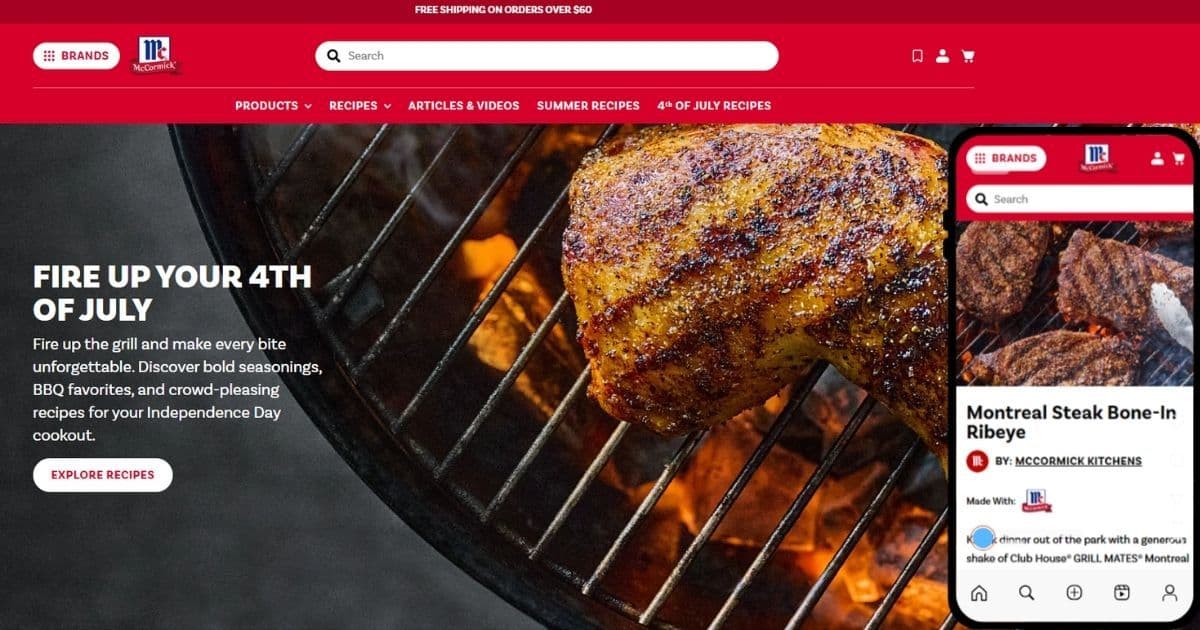
McCormick & Company
What changed on McCormick's front endThe front end now loads non-essential scripts after the main content, runs third-party tags through...
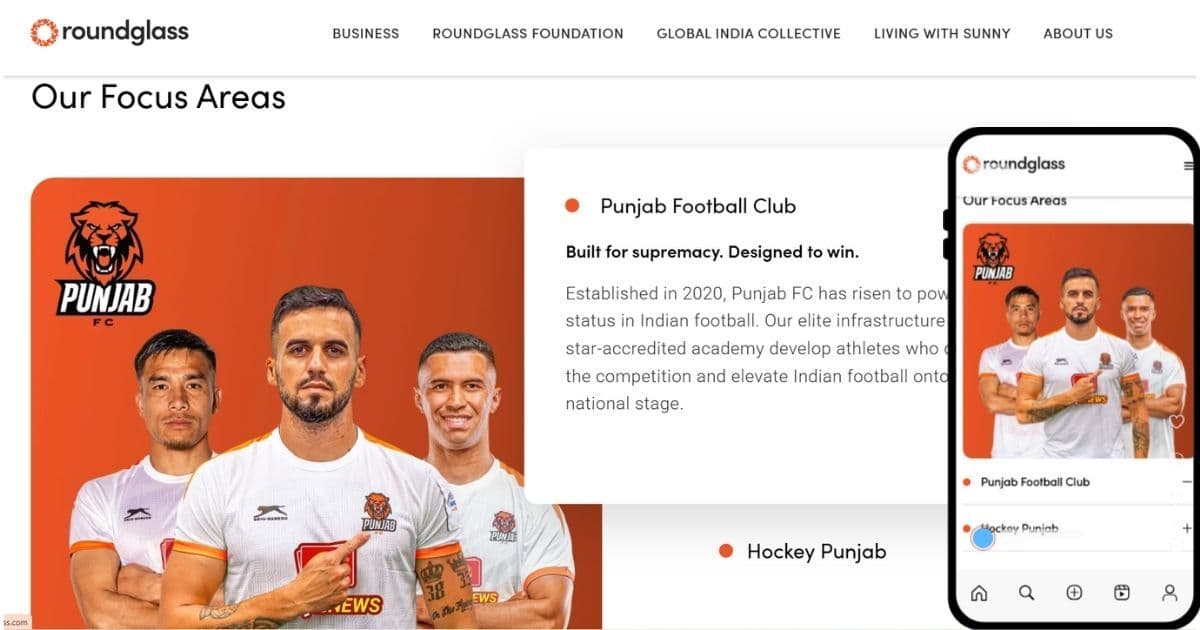
Roundglass
What changed for Roundglass's HR team, IT and new employeesAccount creation, group membership and licence assignment now follow the...
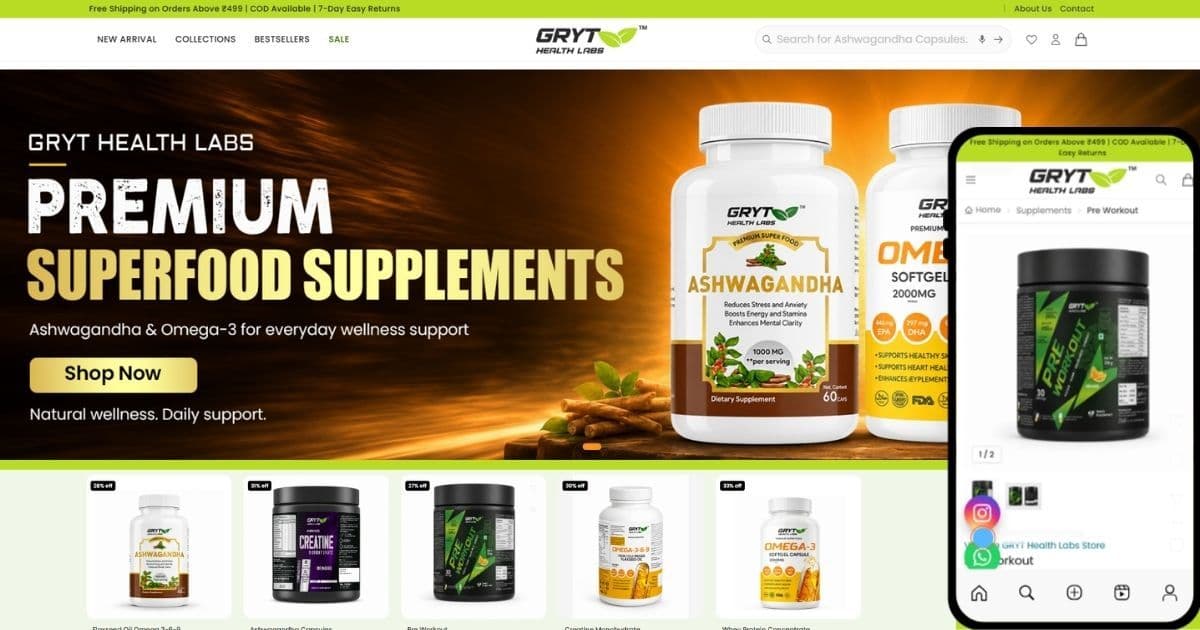
GRYT Health Labs
What GRYT shoppers can do on the storeShoppers can check the brand's licence and ownership details, compare single units with packs of...
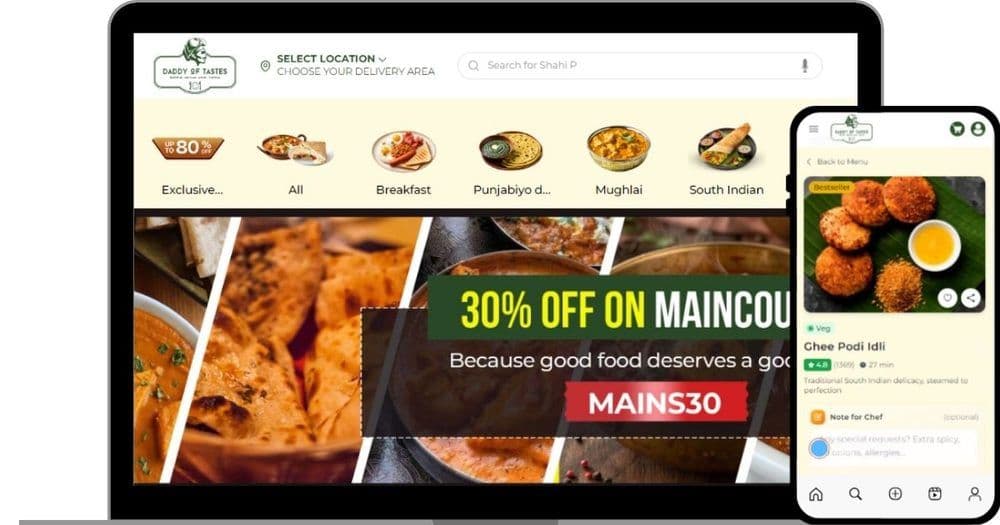
Daddy of Tastes
What the Daddy of Tastes kitchens and riders work withCustomers can order from the full menu, pin their exact location, pay through...
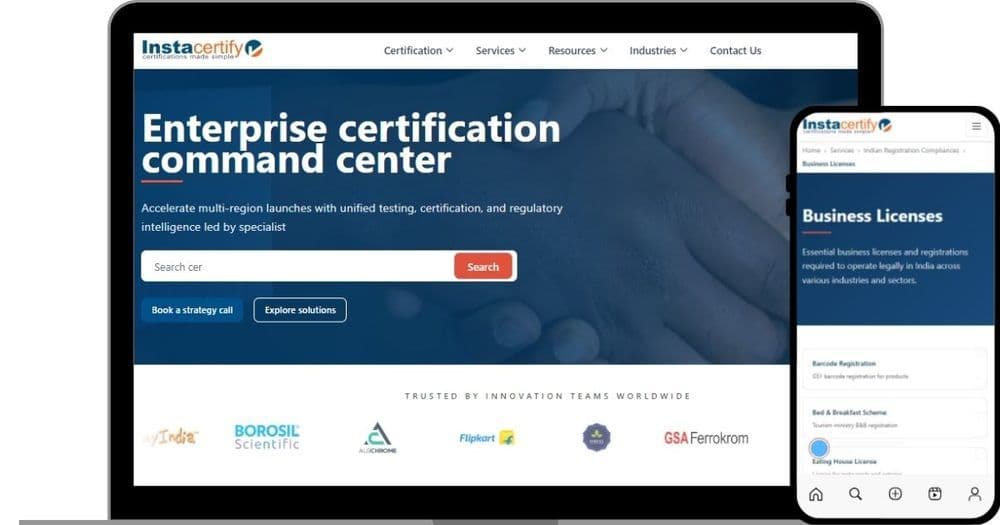
Instacertify
What Instacertify's visitors could doVisitors could search for a certification from the first screen, see two clear next steps, and move...
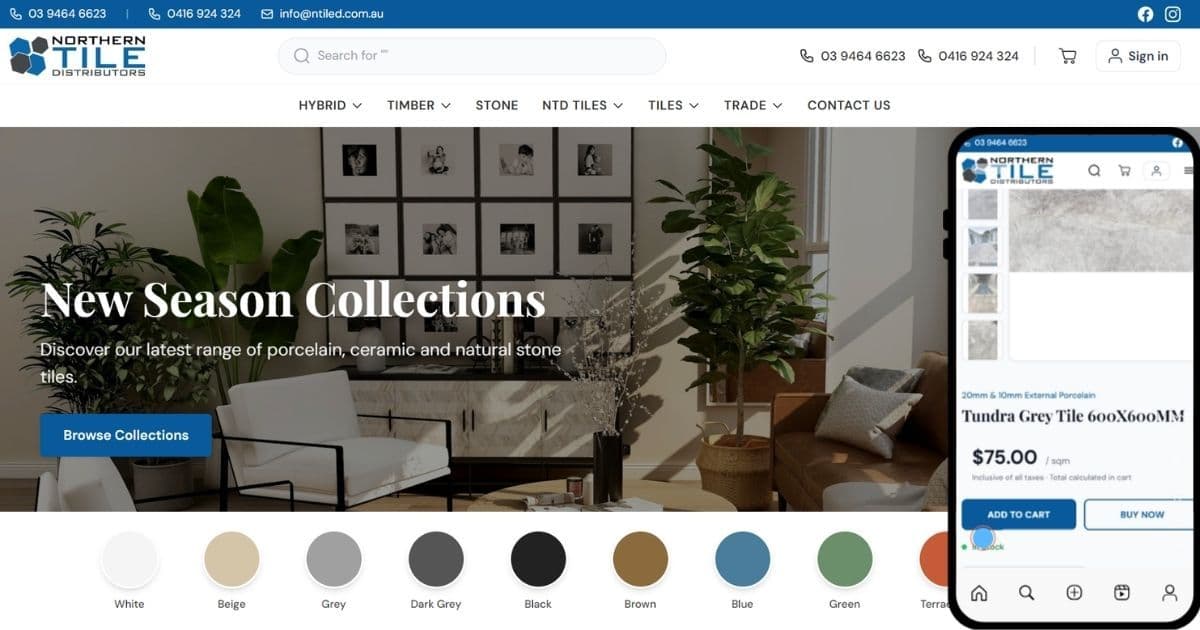
Northern Tile Distributors
The storefront delivers a clean shopping experience on both desktop and mobile. Page load times improved significantly, the add-to-cart rate...
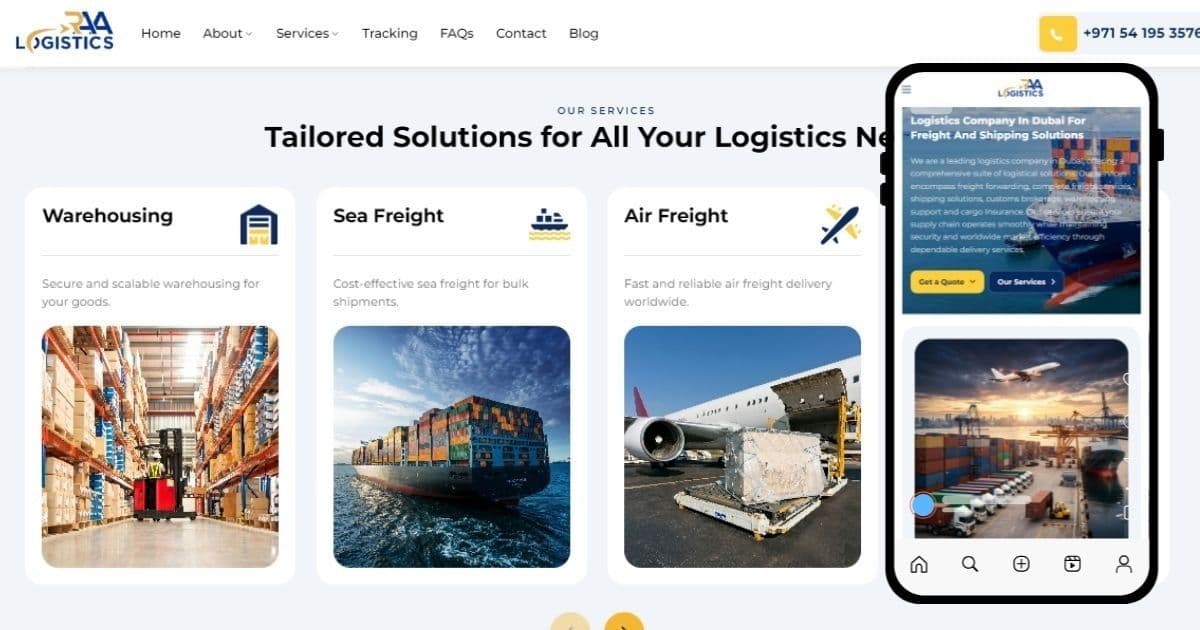
RAA Logistics
What RAA's customers and team have nowProspective customers can find the exact service they need, read what it covers, see who runs the...
Your data protection Score is free. The 90-day plan is yours to keep.
Across our active compliance retainers, the median 12-month exposure we measure for teams with no structured data protection program, from breach cleanup to missed GDPR and PCI DSS obligations, lands in the Rs 6L to Rs 90L band. Book the scoping call to size yours.
Free five-axis Dcrayon data protection Score, gaps ranked by risk
Written 90-day plan tied to one privacy or security metric you pick
Exit-friendly SoW with no annual lock-in
A named GDPR consultant on the account from the start
Data Protection Strategy FAQs
Onboarding begins after a scoping call and access provisioning. Post-incident and breach-response work is prioritized ahead of routine data privacy engagements.
Both. Some clients hand us the whole data protection function, acting as their outsourced DPO and PCI DSS lead. Others keep an internal team and use us as senior GDPR and PCI escalation. We scope per account.
Most data protection strategy engagements start at Rs 4 to 8 lakhs per month in India or USD 6 to 15 thousand per month globally. A one-off GDPR or PCI DSS gap audit starts lower.
Yes. A free five-axis data protection Score on every proposal call, with the top gaps ranked by risk. No follow-on commitment required.
Ready to Grow Your Business?
Get expert digital marketing that delivers measurable results. Free consultation available.
We will review how your search, paid and marketplace channels are performing, and point out the gaps costing you the most right now.
You will finish the call knowing what to fix first, whether or not you work with us.